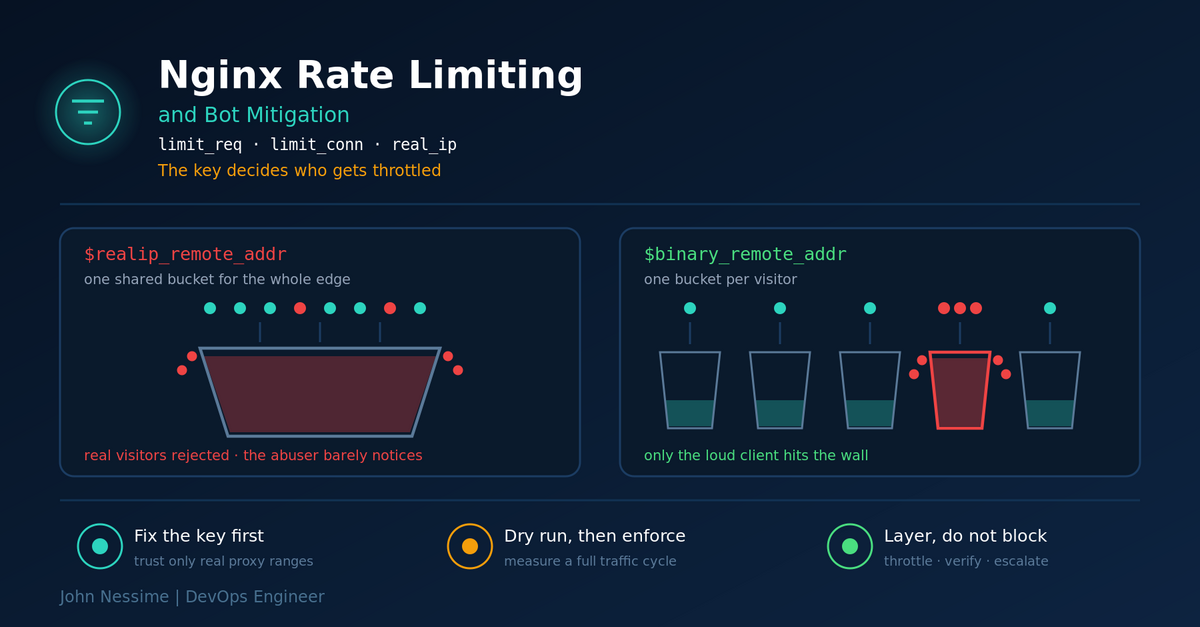
Nginx Rate Limiting and Bot Mitigation Without Blocking Real Users

A limit_req block that parses cleanly can still be doing absolutely nothing, or throttling every visitor behind one CDN edge. This guide covers Nginx rate limiting and bot mitigation as they actually behave in production: getting the key right behind a proxy, what burst and nodelay do to your traffic shape, sizing zones correctly, rolling out in dry run mode, and layering bot handling from robots.txt through user agent maps to firewall escalation.
Continue ReadingNginx Rate Limiting and Bot Mitigation Without Blocking Real Users

Docker Logs Ate My Disk: A Working Guide to Log Drivers and Rotation

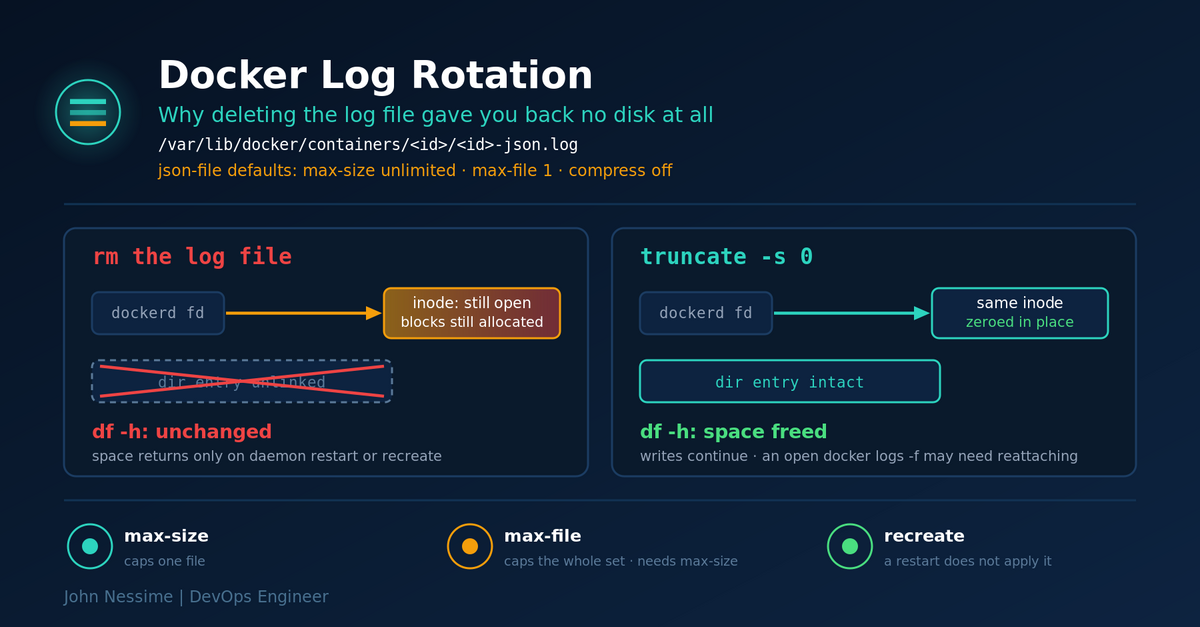
Docker's default logging driver writes container output to a JSON file with no size limit and no rotation. This is a practical guide to Docker log rotation: what the defaults actually do, why your daemon.json change did nothing, why deleting the log file did not free any disk, and how to choose between json-file, local, journald and shipping logs off the box.

Continue ReadingDocker Logs Ate My Disk: A Working Guide to Log Drivers and Rotation

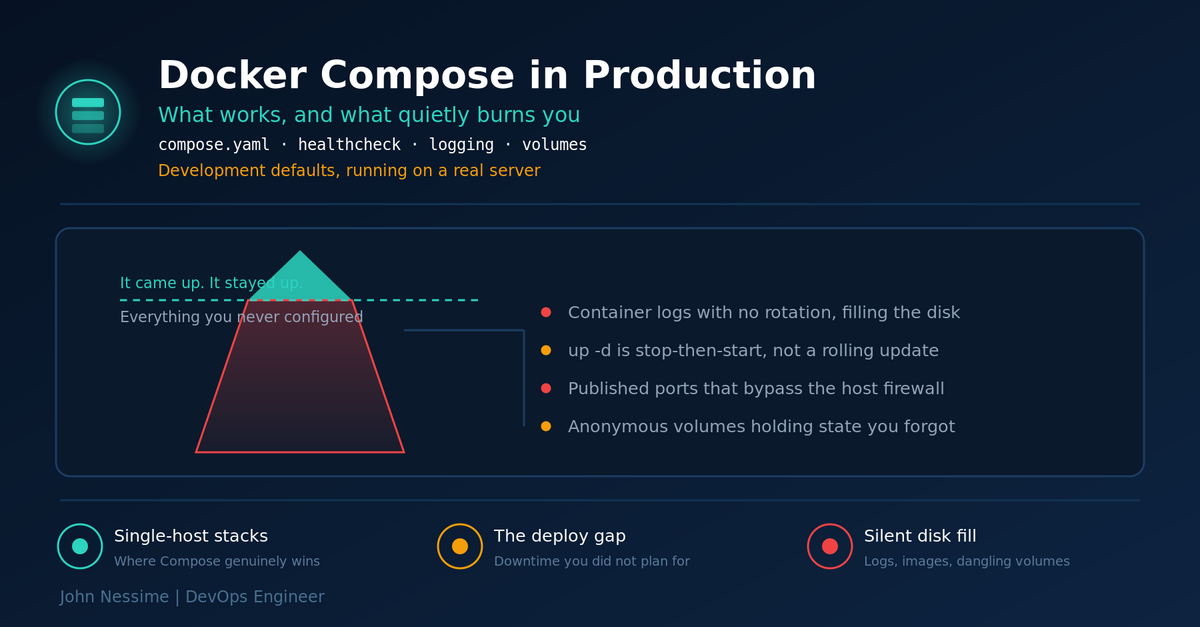
Docker Compose in Production: What Works and What Quietly Burns You

Running Docker Compose in production is a reasonable choice for a single host, but the defaults were chosen for a laptop. A walk through the failure families that actually bite: the deploy gap, unrotated logs filling the disk, anonymous volumes, published ports that bypass your firewall, secrets in environment variables, and health checks that report without acting.

Continue ReadingDocker Compose in Production: What Works and What Quietly Burns You

Build a Secure AI Medical Assistant on AWS: The Boundaries That Actually Leak

A practical architecture for a secure AI medical assistant on AWS, organised by the boundary the data crosses: the input box, your own invocation logs, cross-Region inference routing, the retrieval index, and clinical accuracy. Includes real commands, the failure modes that stay invisible until an audit, and the trade-offs worth knowing before you build.

Continue ReadingBuild a Secure AI Medical Assistant on AWS: The Boundaries That Actually Leak

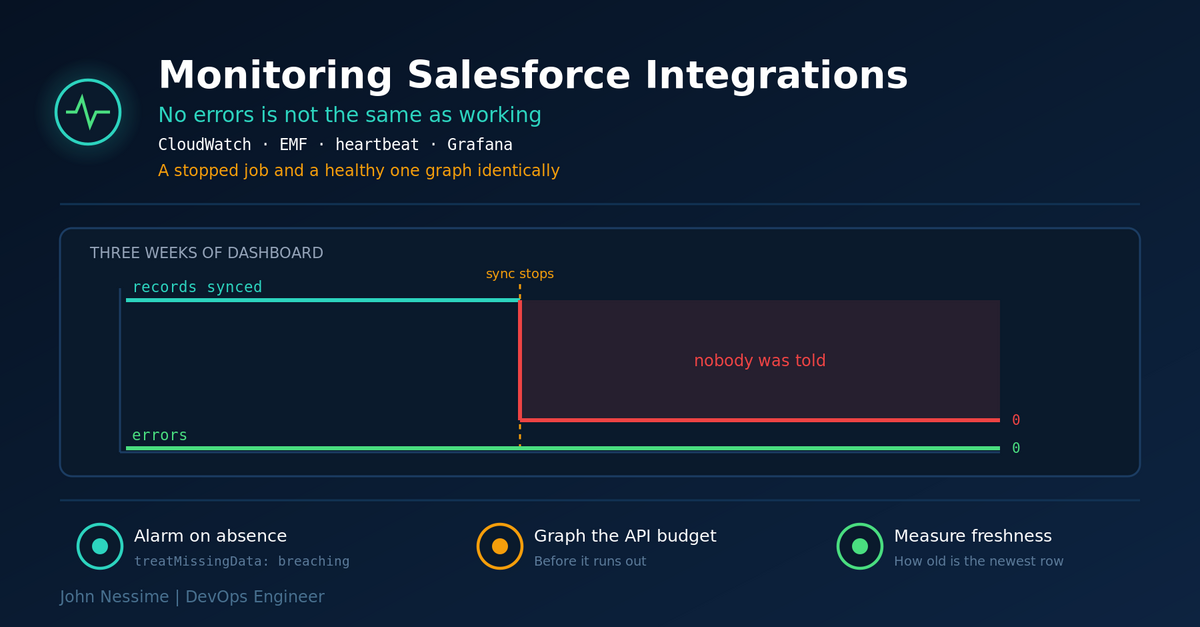
Zero Errors, Zero Records: Monitoring Salesforce Integrations with CloudWatch and Grafana

The error count was zero every day for three weeks. So was the invocation count. A stopped integration and a healthy one produce identical graphs, and every CloudWatch default is tuned to stay quiet when data stops arriving. Four signals worth emitting, and the alarm config that actually fires.

Continue ReadingZero Errors, Zero Records: Monitoring Salesforce Integrations with CloudWatch and Grafana

HIPAA Compliance on AWS: The Gaps That Pass Every Security Check

A working engineer's guide to HIPAA compliance on AWS, organised by the gap between the control you configured and the obligation you actually carry. Covers BAA account scope, the eligible services list as a contract boundary, KMS key policy versus the encryption checkbox, what "six years" really applies to, backup and restore scope, and the subprocessor chain nobody inventories.

Continue ReadingHIPAA Compliance on AWS: The Gaps That Pass Every Security Check