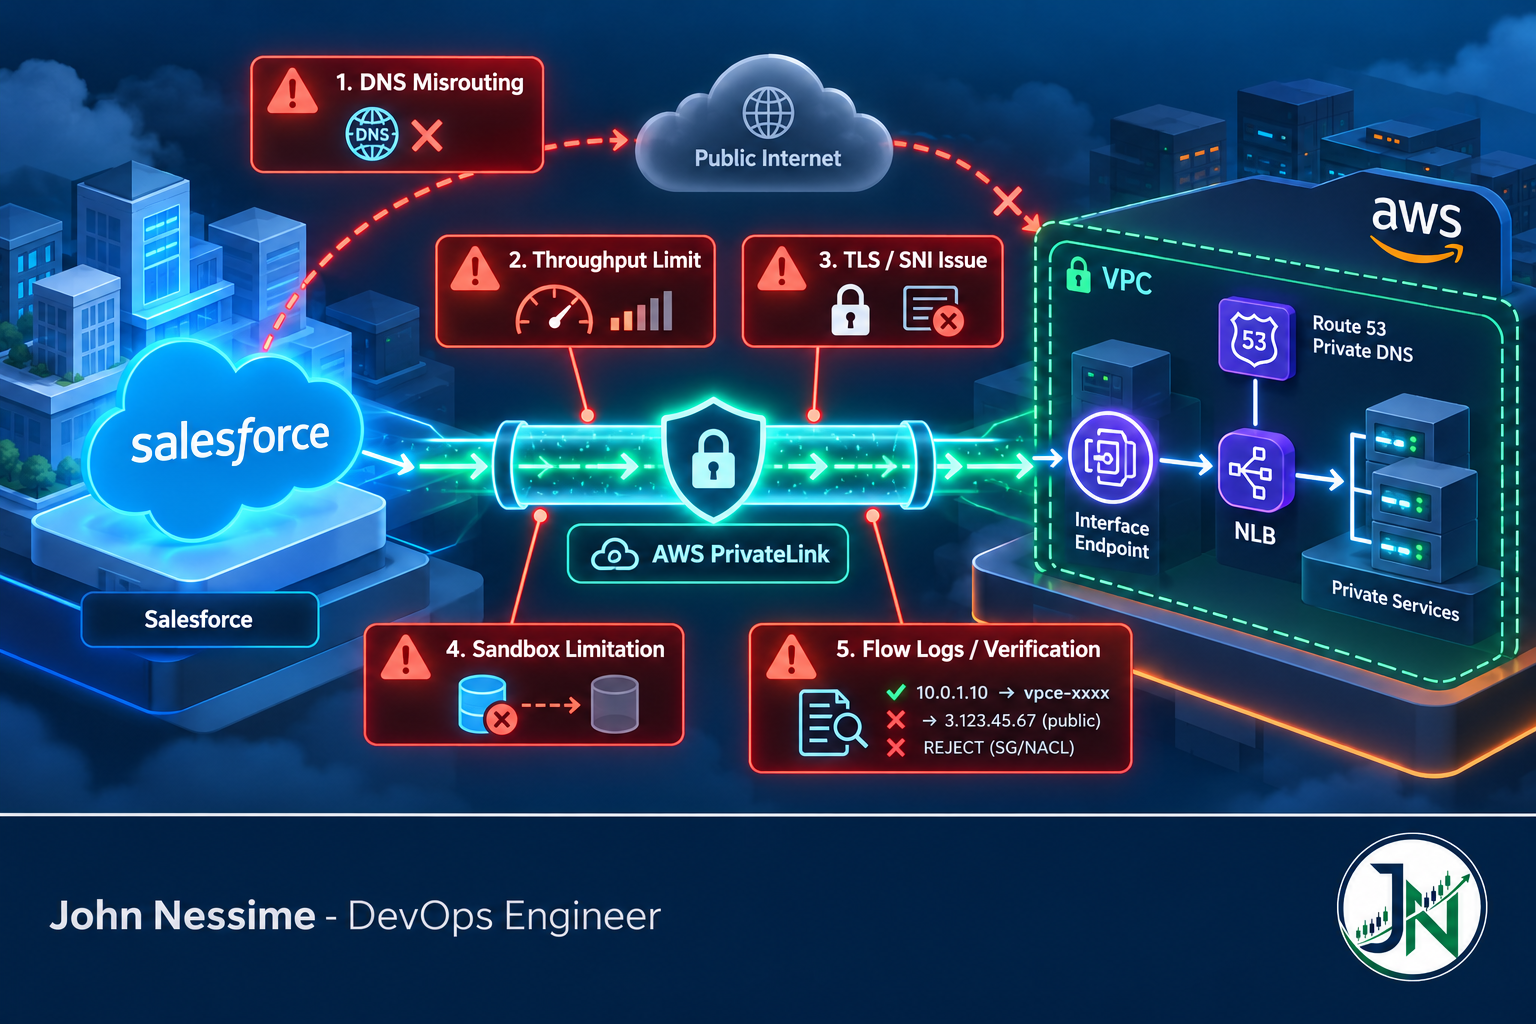
Salesforce AWS PrivateLink: The Failures Nobody Warns You About

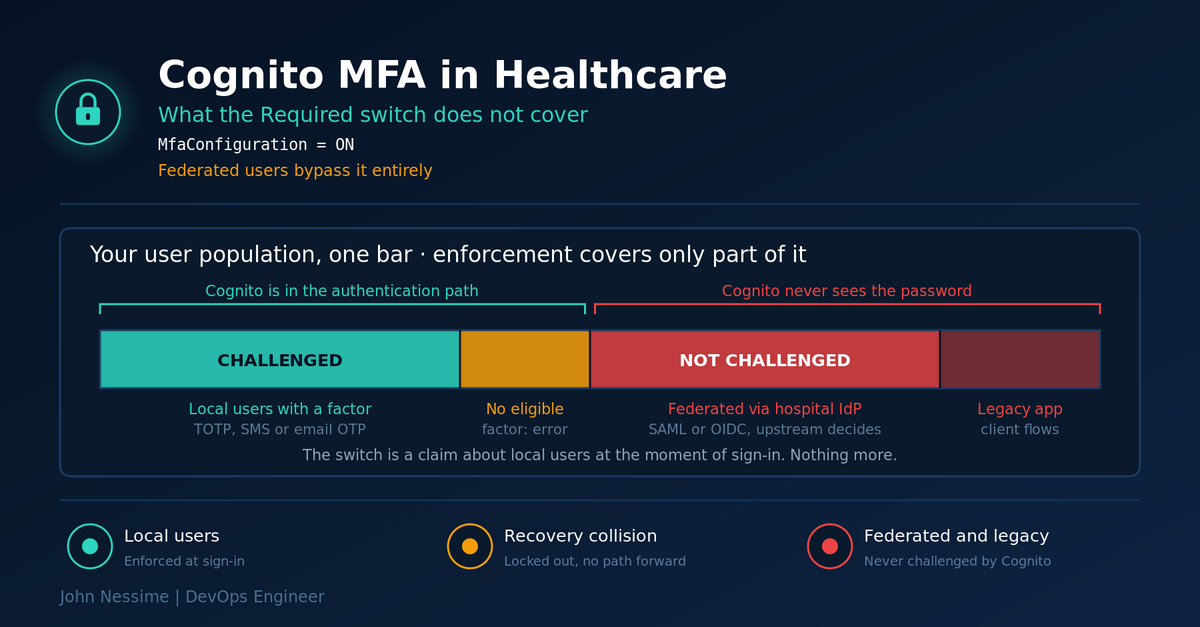
Salesforce Private Connect over AWS PrivateLink does not fail loudly. It fails by working: green statuses, successful callouts, and packets still crossing the public internet because one DNS record was wrong. Here are the six failure families that actually bite, and how to prove your traffic is private.
Continue ReadingSalesforce AWS PrivateLink: The Failures Nobody Warns You About
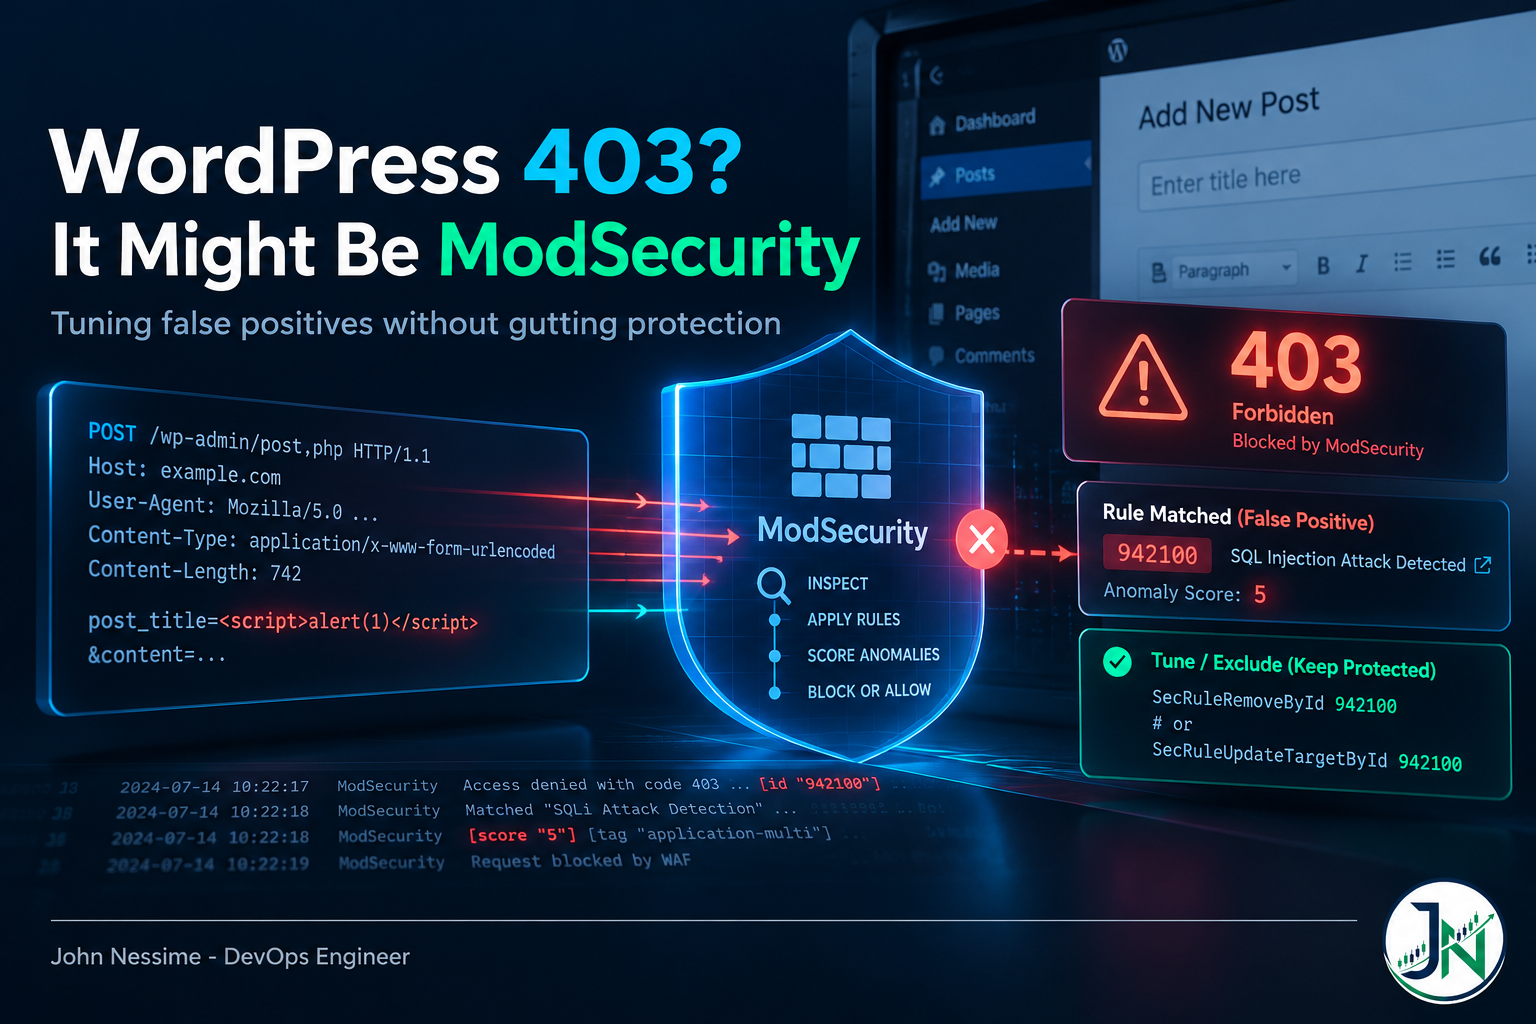
Read more about the article Your WordPress 403 Isn’t the Rule You Think: Tuning ModSecurity False Positives
A WordPress 403 error isn't always caused by a malicious request. ModSecurity false positives can block legitimate updates. Inspect anomaly scores and tune specific WAF rules without weakening site security.

Your WordPress 403 Isn’t the Rule You Think: Tuning ModSecurity False Positives

A 403 from ModSecurity almost never names the rule you need to change. Under anomaly scoring, detection rules only add to a score and a separate blocking rule returns the error. This guide covers reading the audit log backwards, choosing between the four exclusion mechanisms, the WordPress failure families that cause most false positives, and why raising the anomaly threshold quietly destroys your coverage.

Continue ReadingYour WordPress 403 Isn’t the Rule You Think: Tuning ModSecurity False Positives

Nginx Rate Limiting and Bot Mitigation Without Blocking Real Users

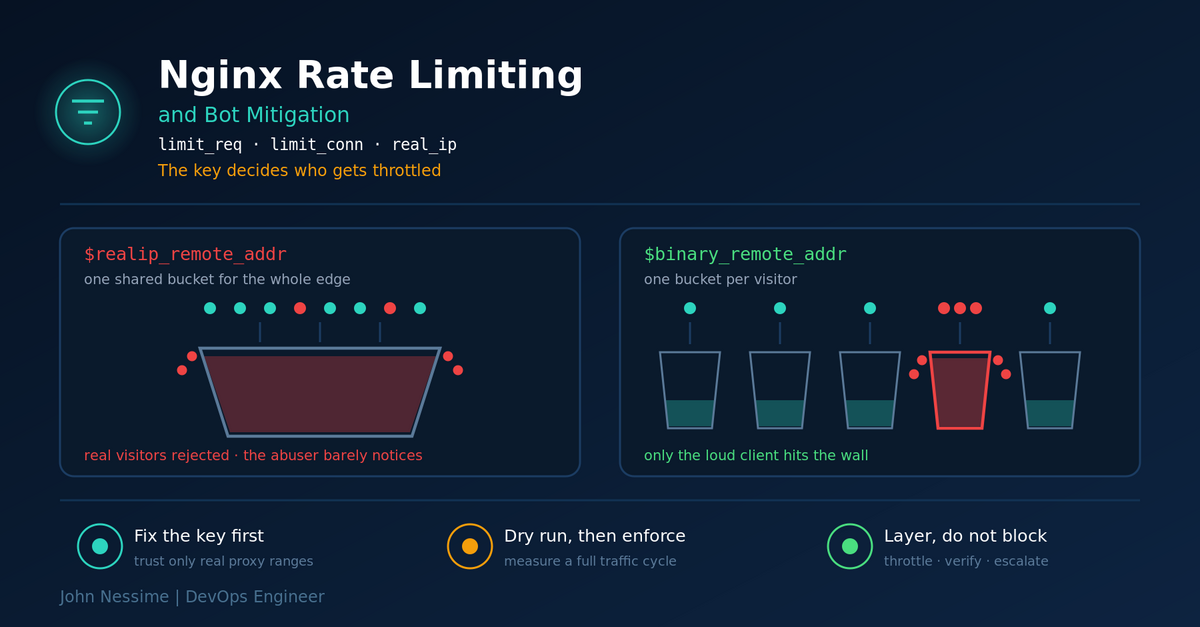
A limit_req block that parses cleanly can still be doing absolutely nothing, or throttling every visitor behind one CDN edge. This guide covers Nginx rate limiting and bot mitigation as they actually behave in production: getting the key right behind a proxy, what burst and nodelay do to your traffic shape, sizing zones correctly, rolling out in dry run mode, and layering bot handling from robots.txt through user agent maps to firewall escalation.

Continue ReadingNginx Rate Limiting and Bot Mitigation Without Blocking Real Users

Business Email DNS Done Right: MX, SPF, DKIM and DMARC

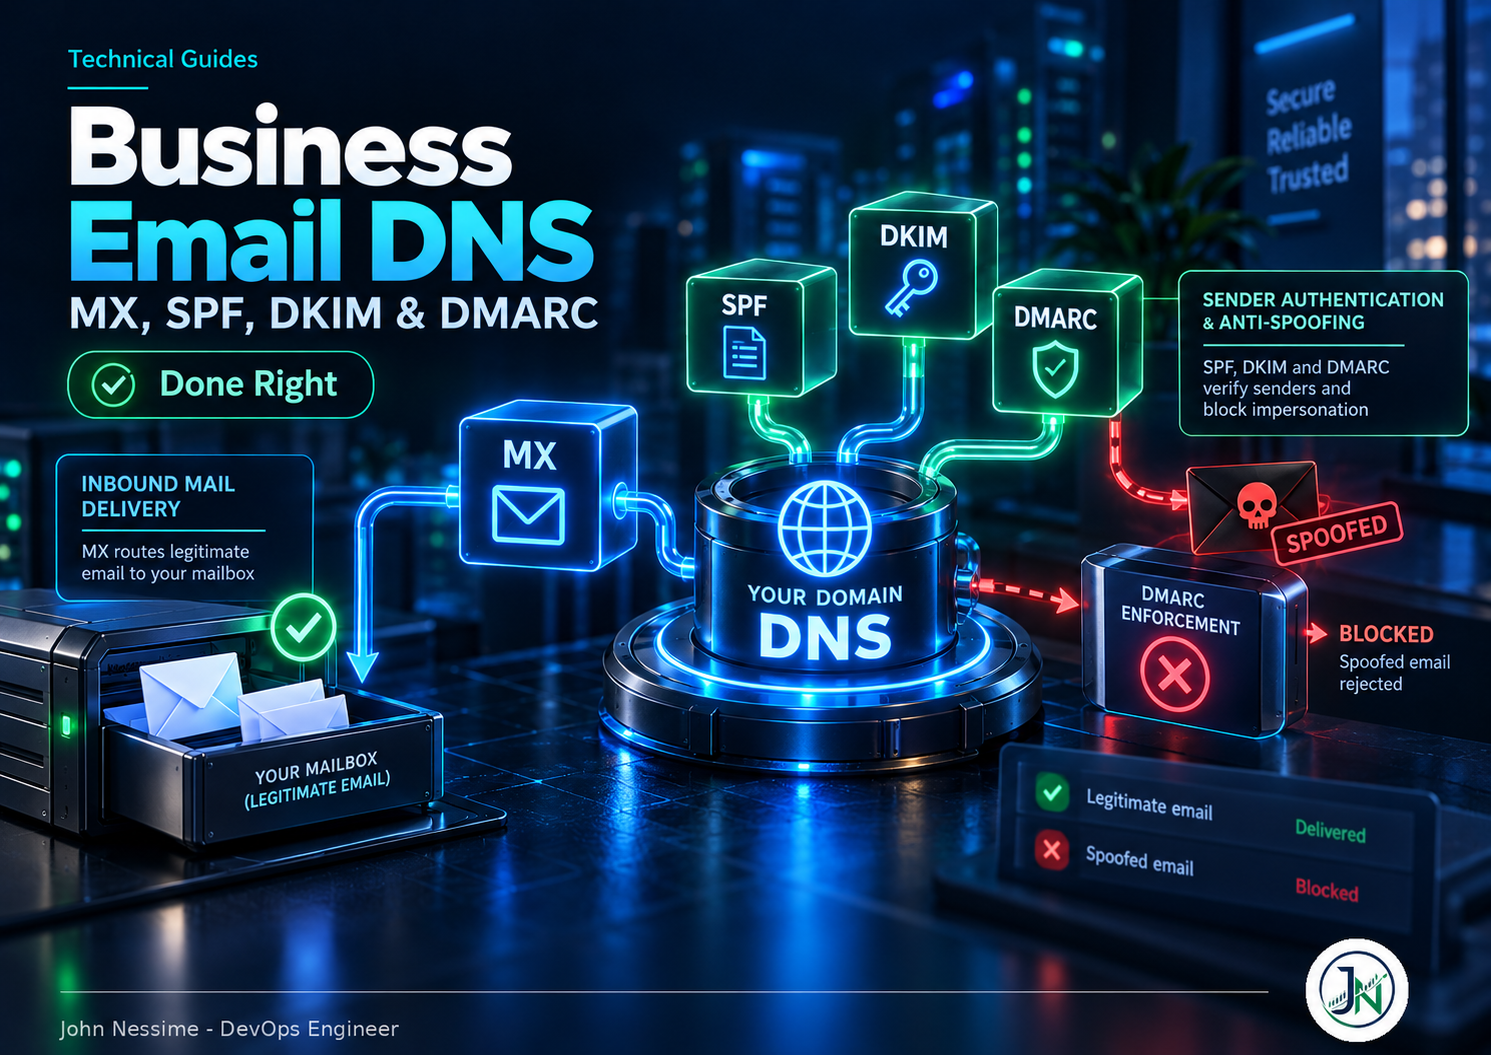
Your domain has all four records. Every free checker shows green. It is still trivially spoofable, because publishing a record and enforcing a policy are different acts. A working guide to business email DNS: what MX, SPF, DKIM and DMARC each actually protect, the SPF lookup budget and the void-lookup limit nobody watches, why DKIM alignment decides whether you can ever reach p=reject, the domain architecture that stops the problem recurring, and a rollout order that gets you to enforcement without losing legitimate mail.

Continue ReadingBusiness Email DNS Done Right: MX, SPF, DKIM and DMARC

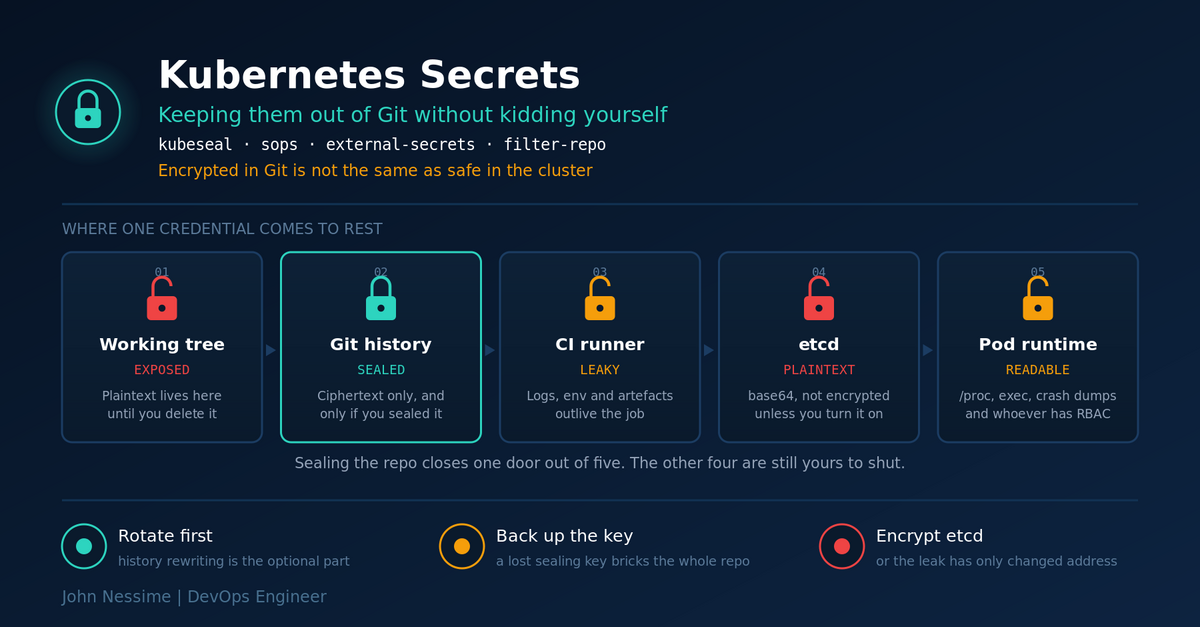
Keep Kubernetes Secrets Out of Git Without Kidding Yourself

Encrypting a Secret before you commit it only closes one of the five places that value comes to rest. Here is how to keep Kubernetes secrets out of Git properly: Sealed Secrets, SOPS and External Secrets compared honestly, the key-backup problem nobody plans for, and what to actually do when a credential is already in your history.

Continue ReadingKeep Kubernetes Secrets Out of Git Without Kidding Yourself

Connect Amazon Redshift to Zoho Analytics Without Putting Your Warehouse on the Internet

Every guide tells you to tick "Publicly Accessible" and move on. That works, and it also puts your warehouse on the internet with whatever credentials were to hand. Here's the full setup done deliberately: least-privilege user, narrow network access, and the outbound-only option nobody mentions.

Continue ReadingConnect Amazon Redshift to Zoho Analytics Without Putting Your Warehouse on the Internet