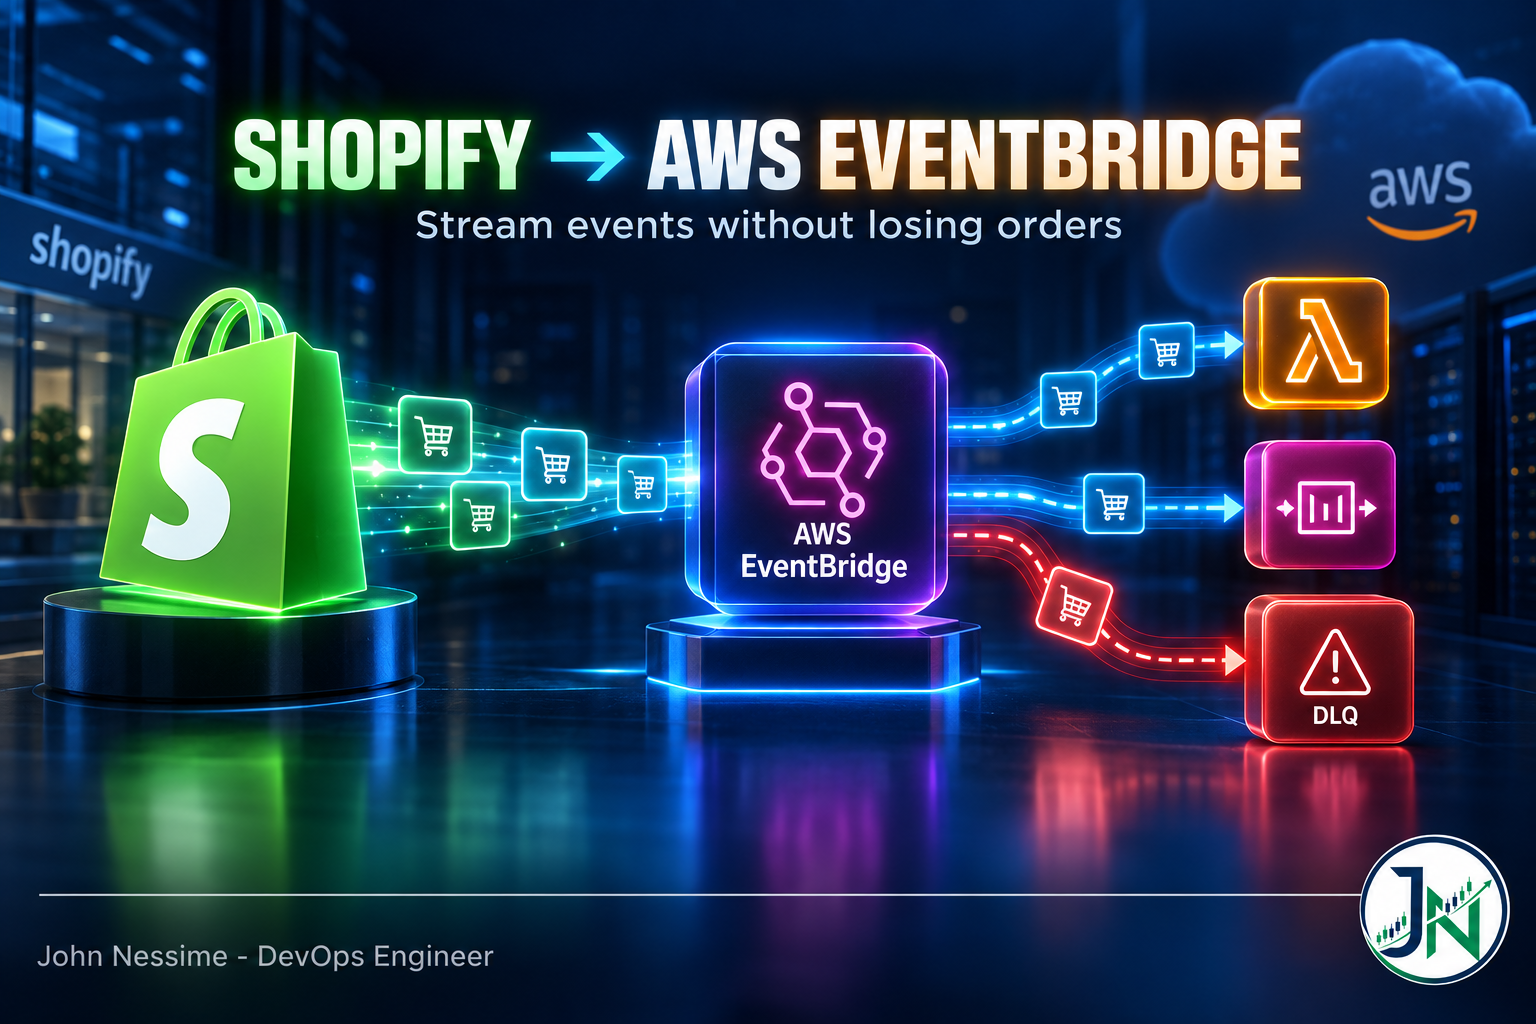
Streaming Shopify Events into AWS Without Losing Orders

Wiring Shopify webhooks into Amazon EventBridge takes an afternoon. Keeping every order is the hard part. A walk through the five failure families that actually bite when streaming Shopify events into AWS: the partner source that silently drops everything, duplicate and out-of-order deliveries, rule patterns that match nothing, targets that fail without a dead-letter queue, and the 64 KB metering rule that quietly inflates the bill.
Continue ReadingStreaming Shopify Events into AWS Without Losing Orders

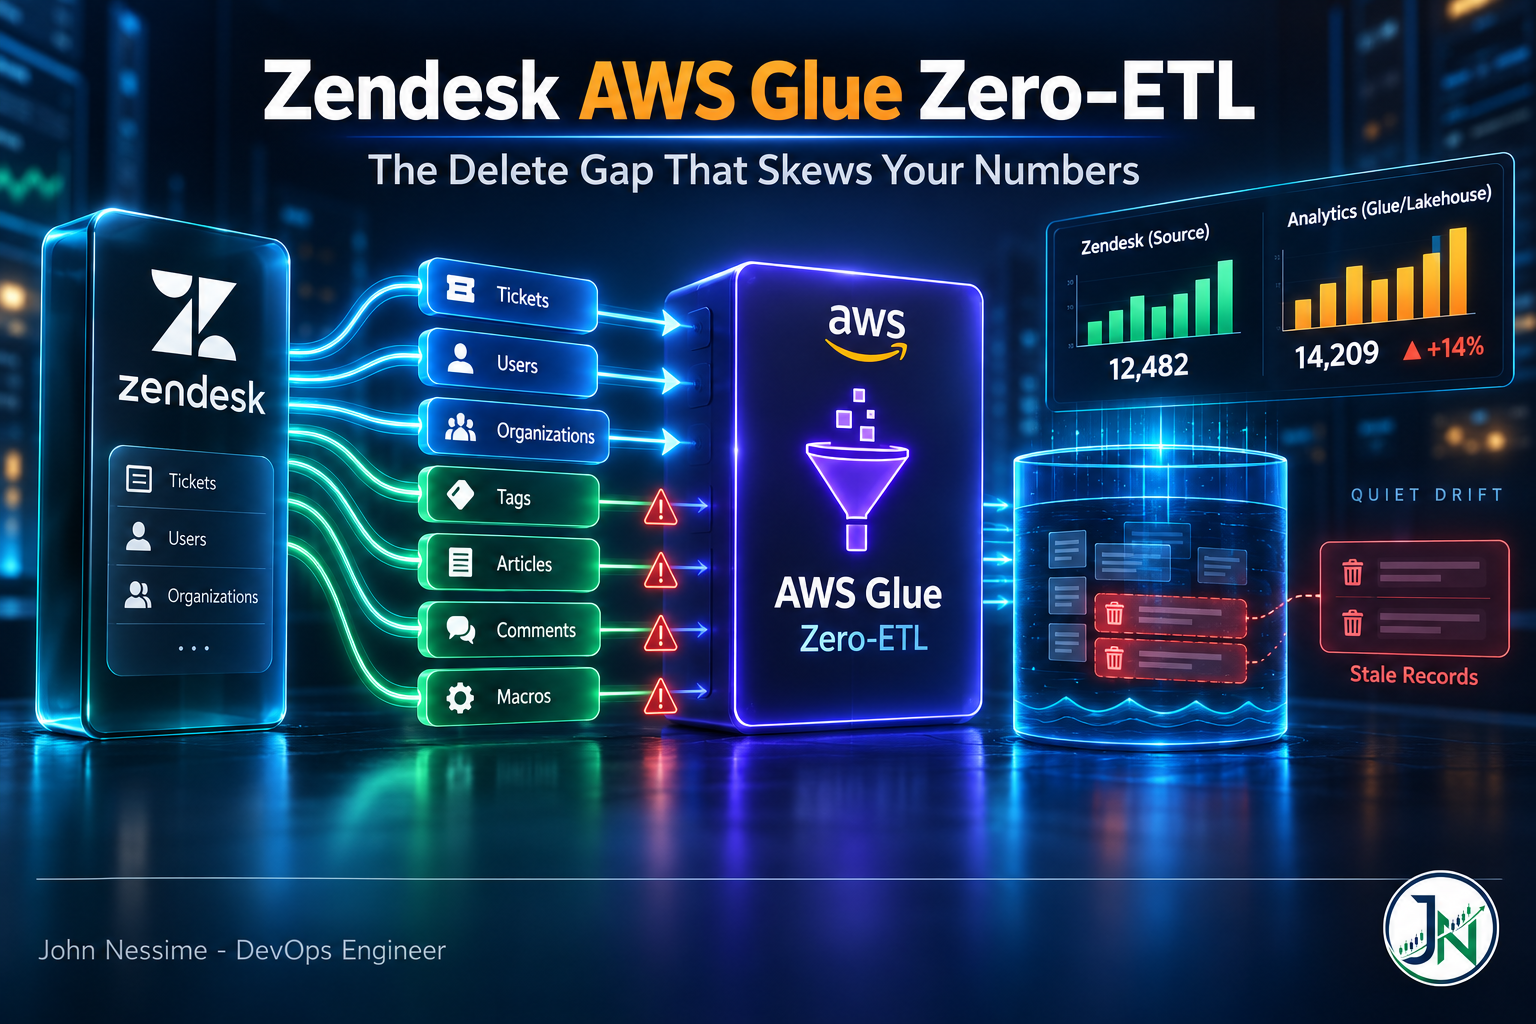
Zendesk Data Integration with AWS Glue Zero-ETL: The Delete Gap That Skews Your Numbers

AWS Glue zero-ETL replicates seven Zendesk entities, but only three of them ever remove a row. Here is how that gap quietly skews CSAT and knowledge base counts, plus the three IAM layers to wire, the two settings you cannot change after creation, and the CloudWatch metrics that make drift visible before someone spots it in a meeting.

Continue ReadingZendesk Data Integration with AWS Glue Zero-ETL: The Delete Gap That Skews Your Numbers

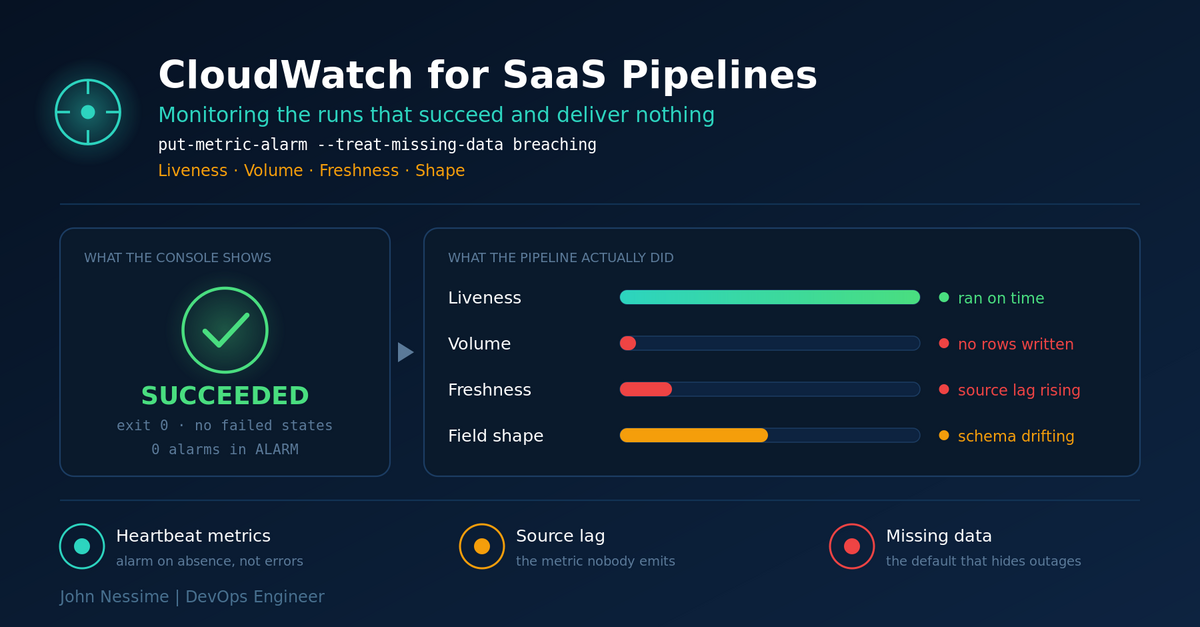
CloudWatch Data Pipeline Monitoring: Catching the Runs That Succeed and Deliver Nothing

Your SaaS pipeline will fail far more often by succeeding at nothing than by throwing an exception, and every CloudWatch default treats an absent metric as a non-event. Here are the four signals worth alarming on: liveness, volume, freshness and shape, plus the missing-data traps that leave alarms permanently green.

Continue ReadingCloudWatch Data Pipeline Monitoring: Catching the Runs That Succeed and Deliver Nothing

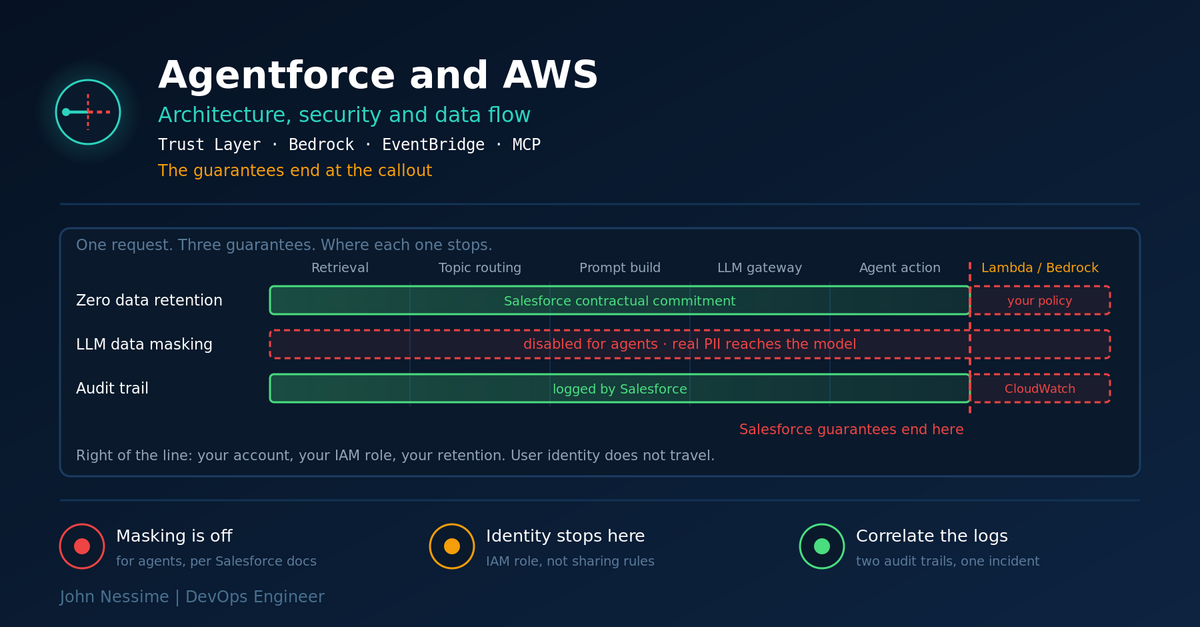
Agentforce and AWS: Where the Trust Layer Stops and Your Logs Begin

Agentforce and AWS wire together in four standard patterns, and every one of them has a point where Salesforce's guarantees stop and yours start. This traces a single request across each boundary it crosses, covers the Trust Layer default most write-ups get wrong (LLM data masking is disabled for agents), and sets out what changes the moment a callout lands in your own account: retention, audit trail, and user identity that does not travel.

Continue ReadingAgentforce and AWS: Where the Trust Layer Stops and Your Logs Begin

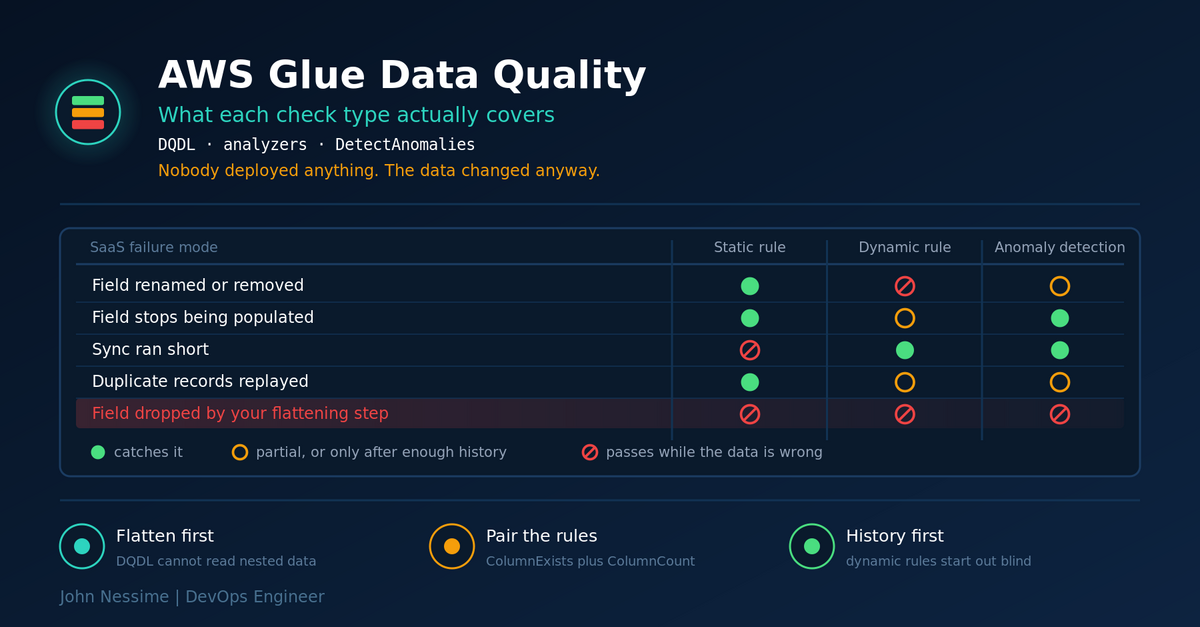
AWS Glue Data Quality for SaaS Data: Catching the Breakage Nobody Deployed

A SaaS admin changes a field and your pipeline stays green while the numbers drift. A practical guide to AWS Glue Data Quality for SaaS sources: where to run the checks, why nested payloads need flattening before DQDL can see them, which rule catches which failure, and the dynamic rules that pass silently because they have no history yet.

Continue ReadingAWS Glue Data Quality for SaaS Data: Catching the Breakage Nobody Deployed

Build a Secure AI Medical Assistant on AWS: The Boundaries That Actually Leak

A practical architecture for a secure AI medical assistant on AWS, organised by the boundary the data crosses: the input box, your own invocation logs, cross-Region inference routing, the retrieval index, and clinical accuracy. Includes real commands, the failure modes that stay invisible until an audit, and the trade-offs worth knowing before you build.

Continue ReadingBuild a Secure AI Medical Assistant on AWS: The Boundaries That Actually Leak

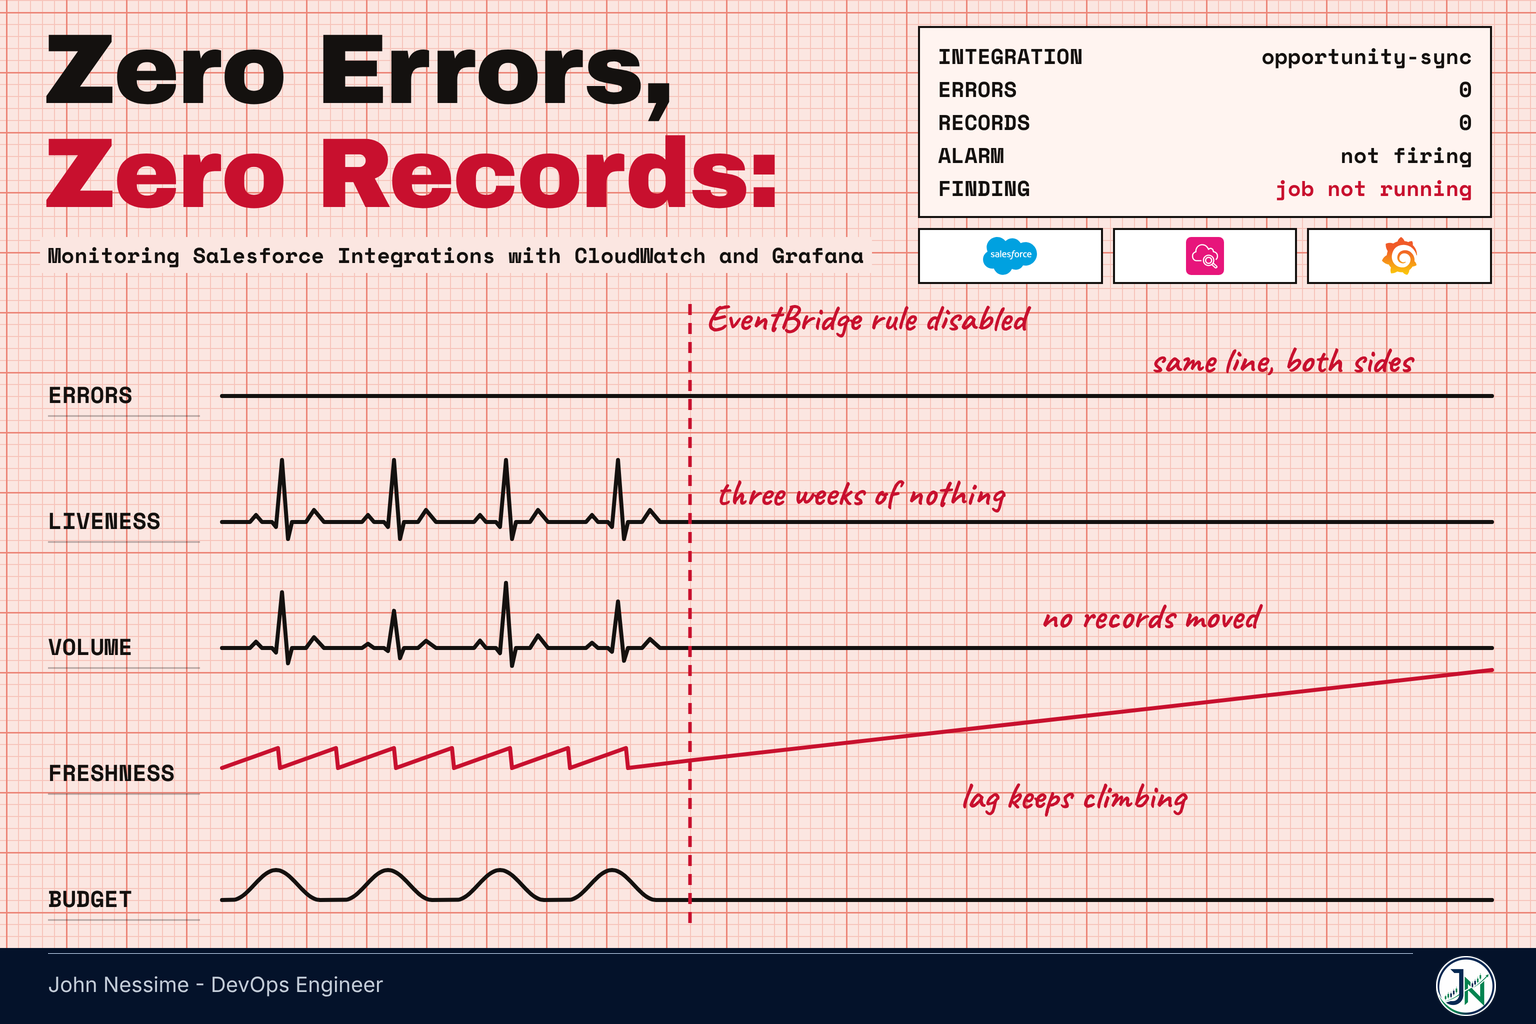
Zero Errors, Zero Records: Monitoring Salesforce Integrations with CloudWatch and Grafana

The error count was zero every day for three weeks. So was the invocation count. A stopped integration and a healthy one produce identical graphs, and every CloudWatch default is tuned to stay quiet when data stops arriving. Four signals worth emitting, and the alarm config that actually fires.

Continue ReadingZero Errors, Zero Records: Monitoring Salesforce Integrations with CloudWatch and Grafana

HIPAA Compliance on AWS: The Gaps That Pass Every Security Check

A working engineer's guide to HIPAA compliance on AWS, organised by the gap between the control you configured and the obligation you actually carry. Covers BAA account scope, the eligible services list as a contract boundary, KMS key policy versus the encryption checkbox, what "six years" really applies to, backup and restore scope, and the subprocessor chain nobody inventories.

Continue ReadingHIPAA Compliance on AWS: The Gaps That Pass Every Security Check