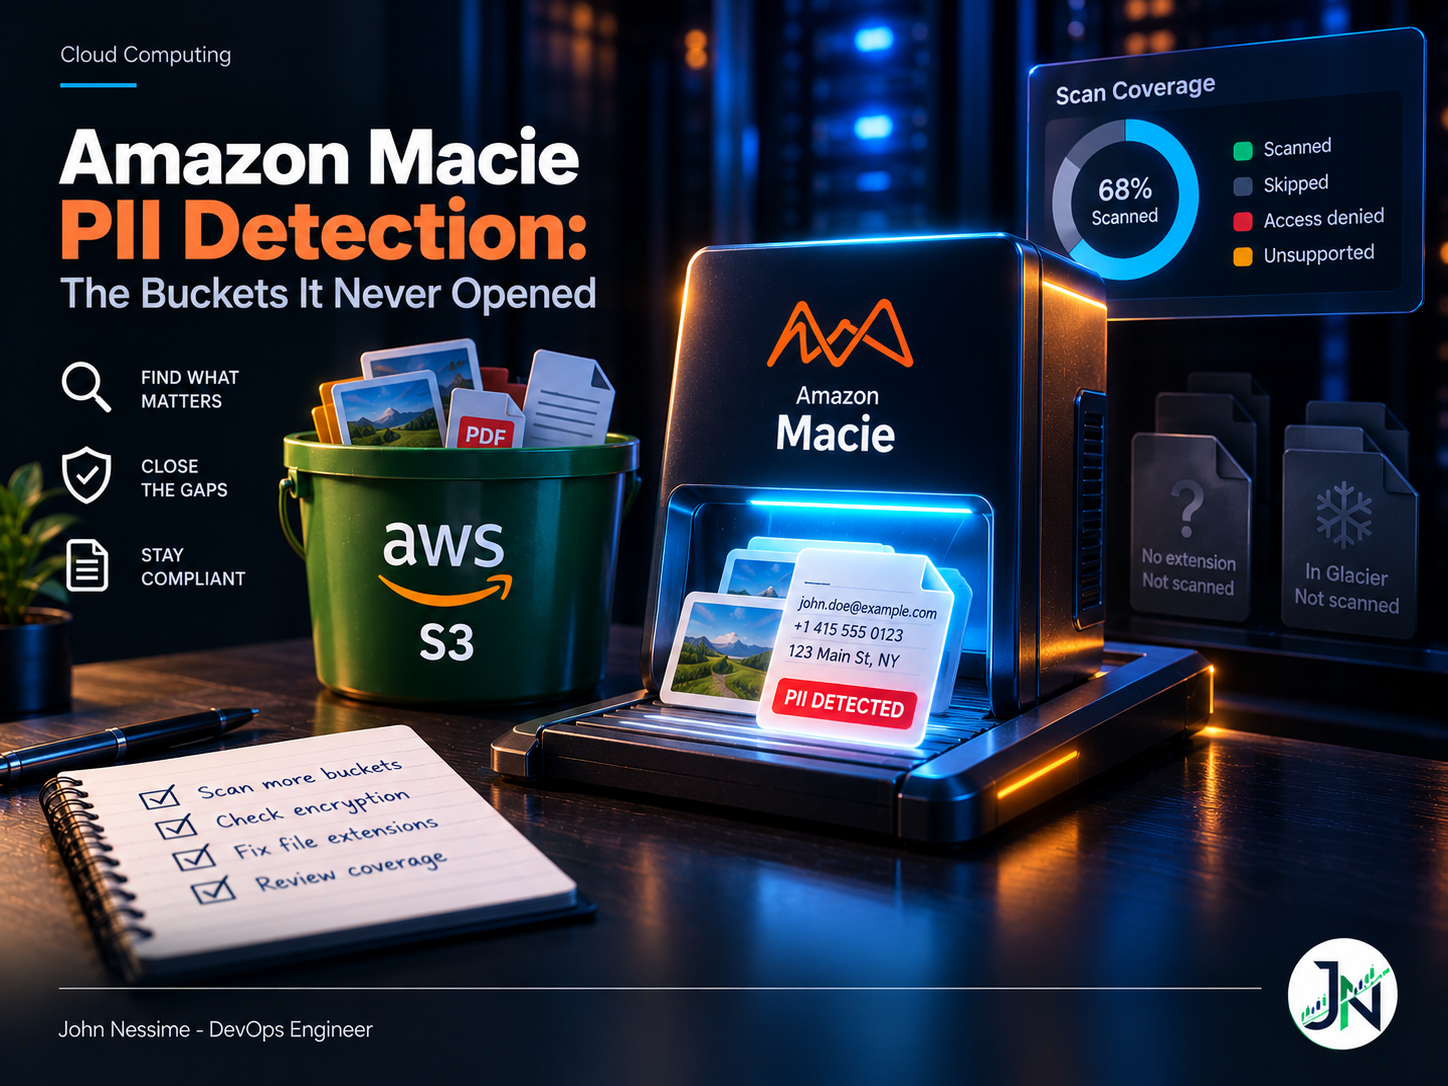
Amazon Macie PII Detection: The Buckets It Never Opened

A Macie bucket labeled "Not sensitive" often just means Macie never read it. Extensionless objects, unsupported storage classes, unreachable KMS keys and quota truncation all produce silence that looks identical to a clean result. Here's how to measure coverage, fix the four gaps, tune identifiers, and keep the bill honest.
Continue ReadingAmazon Macie PII Detection: The Buckets It Never Opened

Building a Secure Client Document Vault Your Accounting Firm Can Defend

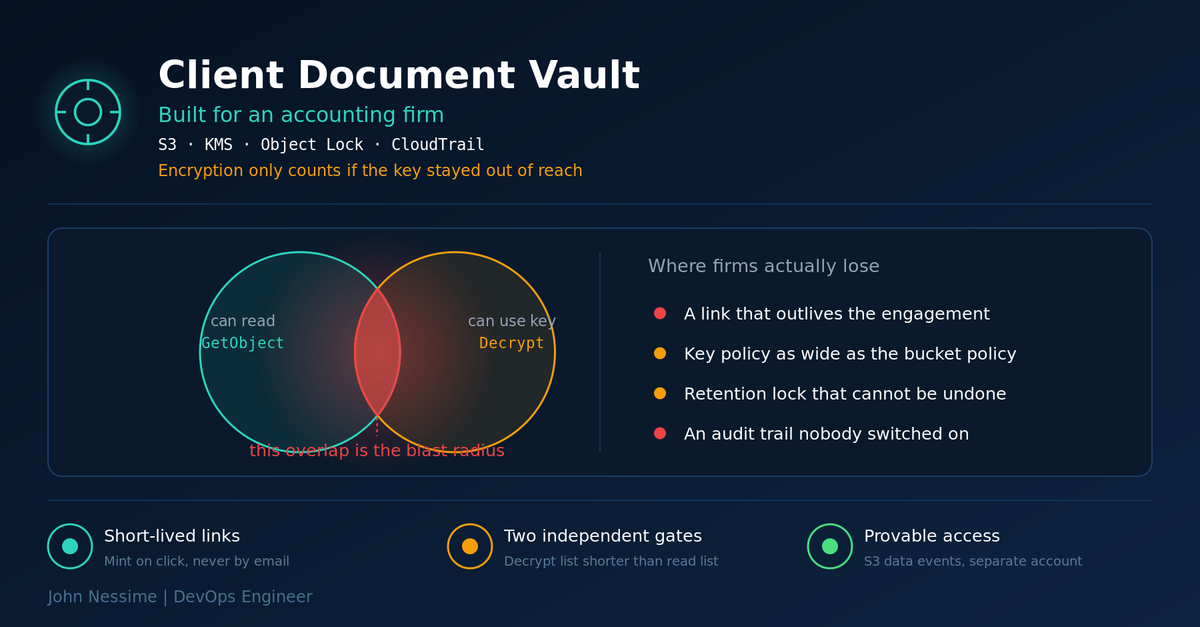
Most accounting-firm document vaults do not fail at the bucket. They fail at the edges: a download link that outlives the engagement, a KMS key policy as wide as the bucket policy, a retention lock that cannot be undone, and an audit trail nobody switched on. Six failure families, and the control that closes each.

Continue ReadingBuilding a Secure Client Document Vault Your Accounting Firm Can Defend

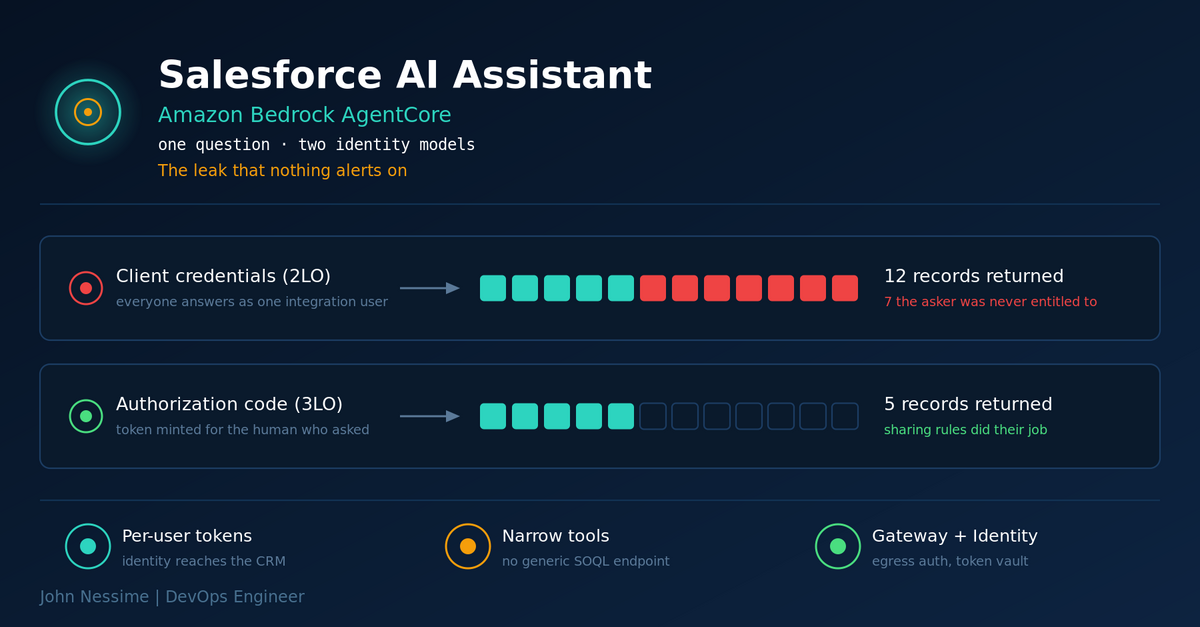
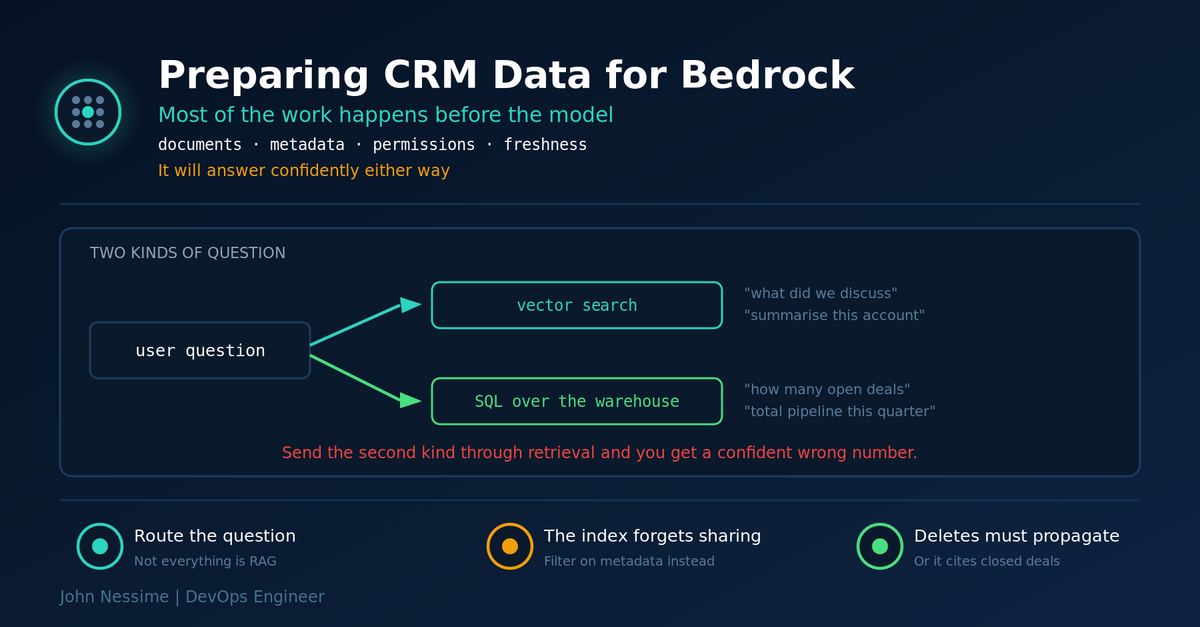
Building a Salesforce AI Assistant on Amazon Bedrock Without Leaking Your CRM

The demo works, then someone sees records they shouldn't. Nothing errors. Here's how to build a Salesforce AI assistant with Amazon Bedrock that respects your sharing model: which doors AWS and Salesforce just closed, why identity propagation is the failure mode that bites, and how to shape the tool surface so the agent can't wander.

Continue ReadingBuilding a Salesforce AI Assistant on Amazon Bedrock Without Leaking Your CRM

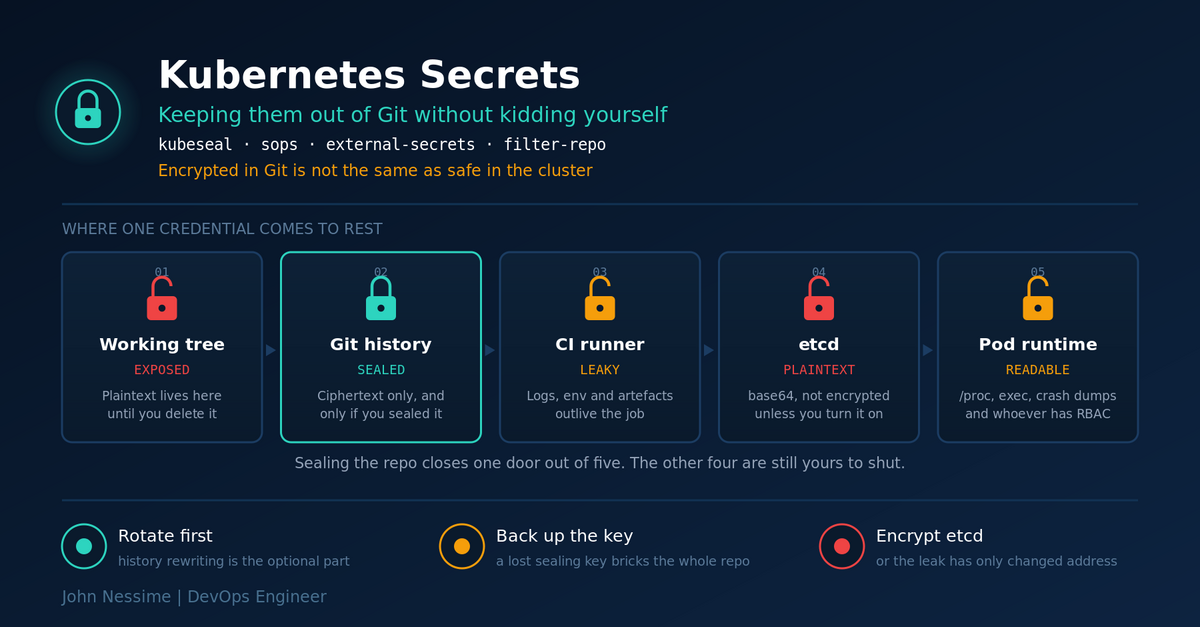
Keep Kubernetes Secrets Out of Git Without Kidding Yourself

Encrypting a Secret before you commit it only closes one of the five places that value comes to rest. Here is how to keep Kubernetes secrets out of Git properly: Sealed Secrets, SOPS and External Secrets compared honestly, the key-backup problem nobody plans for, and what to actually do when a credential is already in your history.

Continue ReadingKeep Kubernetes Secrets Out of Git Without Kidding Yourself

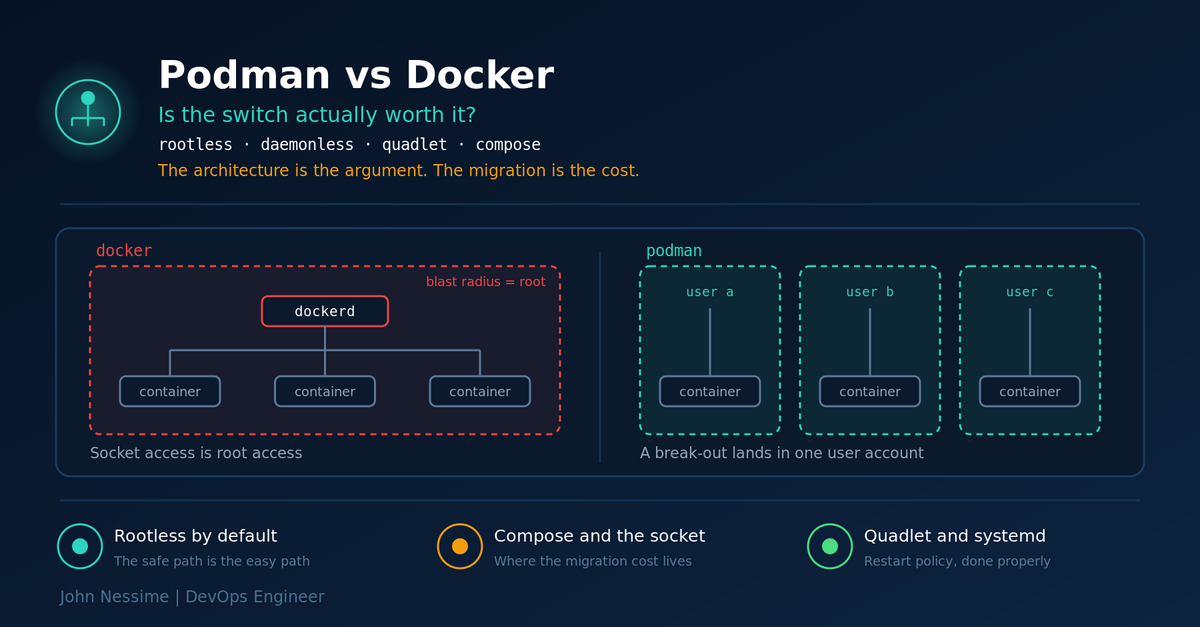
Podman vs Docker: Is the Switch Actually Worth It?

Podman is the better-designed container engine and Docker is the better-supported one. A working engineer's comparison: the architectural difference that drives everything, where each one wins and loses, the four things that genuinely break in a migration (compose, the Docker socket, privileged ports, restart on boot), and a decision procedure to run against your own setup.

Continue ReadingPodman vs Docker: Is the Switch Actually Worth It?

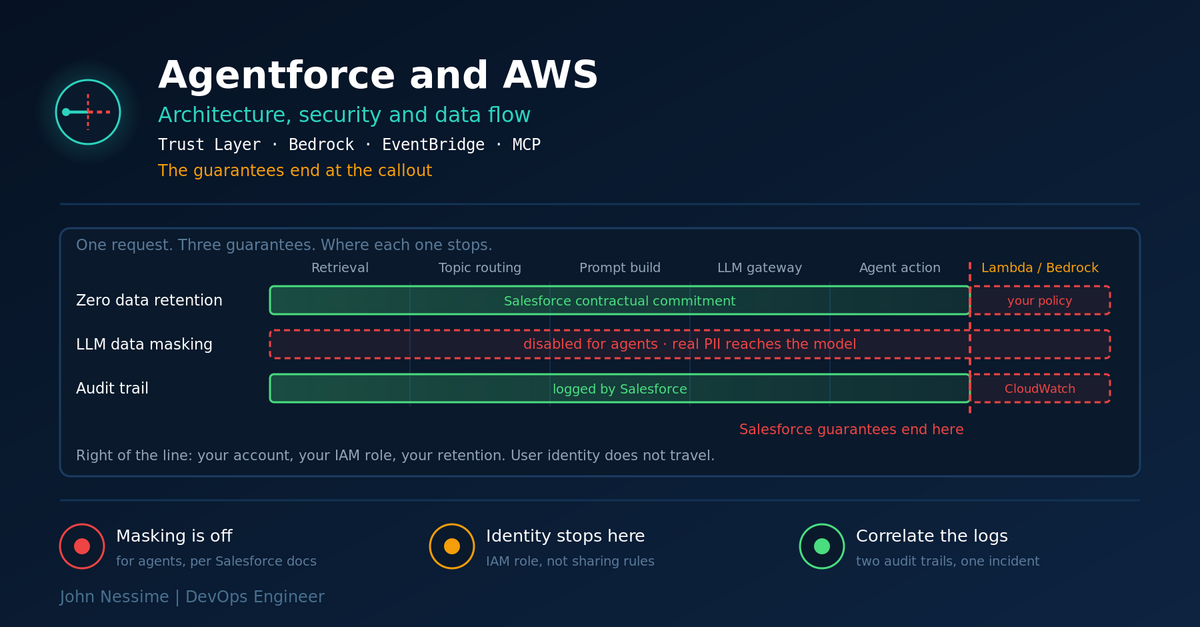
Agentforce and AWS: Where the Trust Layer Stops and Your Logs Begin

Agentforce and AWS wire together in four standard patterns, and every one of them has a point where Salesforce's guarantees stop and yours start. This traces a single request across each boundary it crosses, covers the Trust Layer default most write-ups get wrong (LLM data masking is disabled for agents), and sets out what changes the moment a callout lands in your own account: retention, audit trail, and user identity that does not travel.

Continue ReadingAgentforce and AWS: Where the Trust Layer Stops and Your Logs Begin