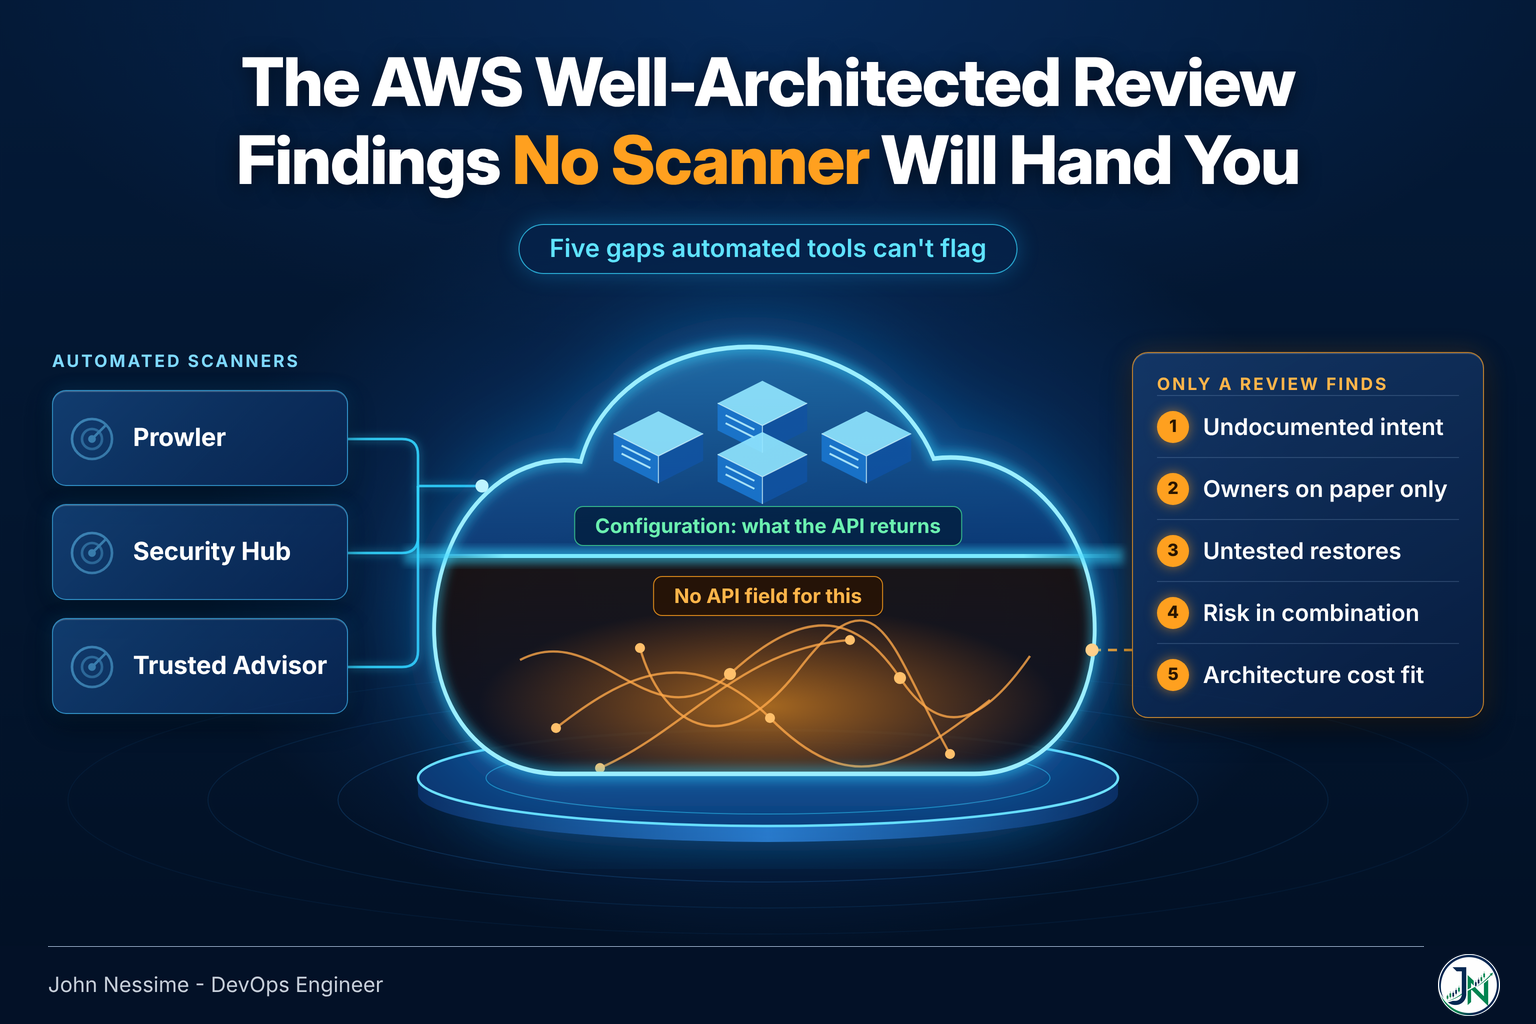
The AWS Well-Architected Review Findings No Scanner Will Hand You

Security Hub is green, Trusted Advisor is green, and the thing that takes the workload down isn't in either report. Five gap families I work through in an AWS Well-Architected review that no configuration scanner can reach: undocumented intent, paper ownership, untested recovery, correlated blast radius, and cost efficiency measured against the wrong architecture.
Continue ReadingThe AWS Well-Architected Review Findings No Scanner Will Hand You

HIPAA Compliance on AWS: The Gaps That Pass Every Security Check

A working engineer's guide to HIPAA compliance on AWS, organised by the gap between the control you configured and the obligation you actually carry. Covers BAA account scope, the eligible services list as a contract boundary, KMS key policy versus the encryption checkbox, what "six years" really applies to, backup and restore scope, and the subprocessor chain nobody inventories.

Continue ReadingHIPAA Compliance on AWS: The Gaps That Pass Every Security Check