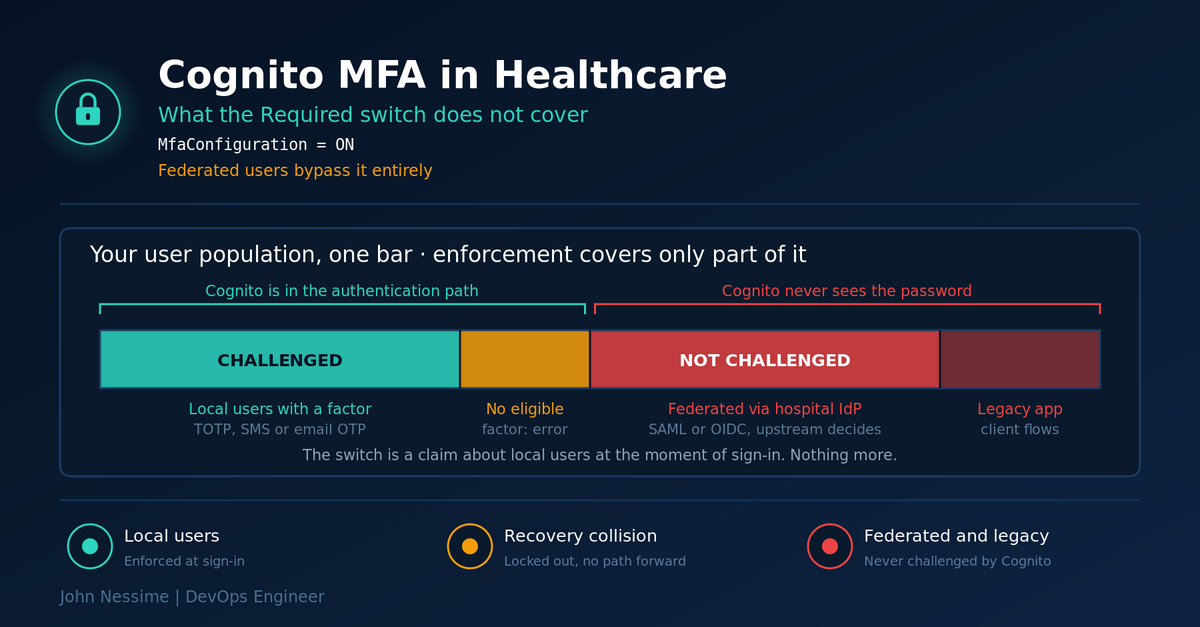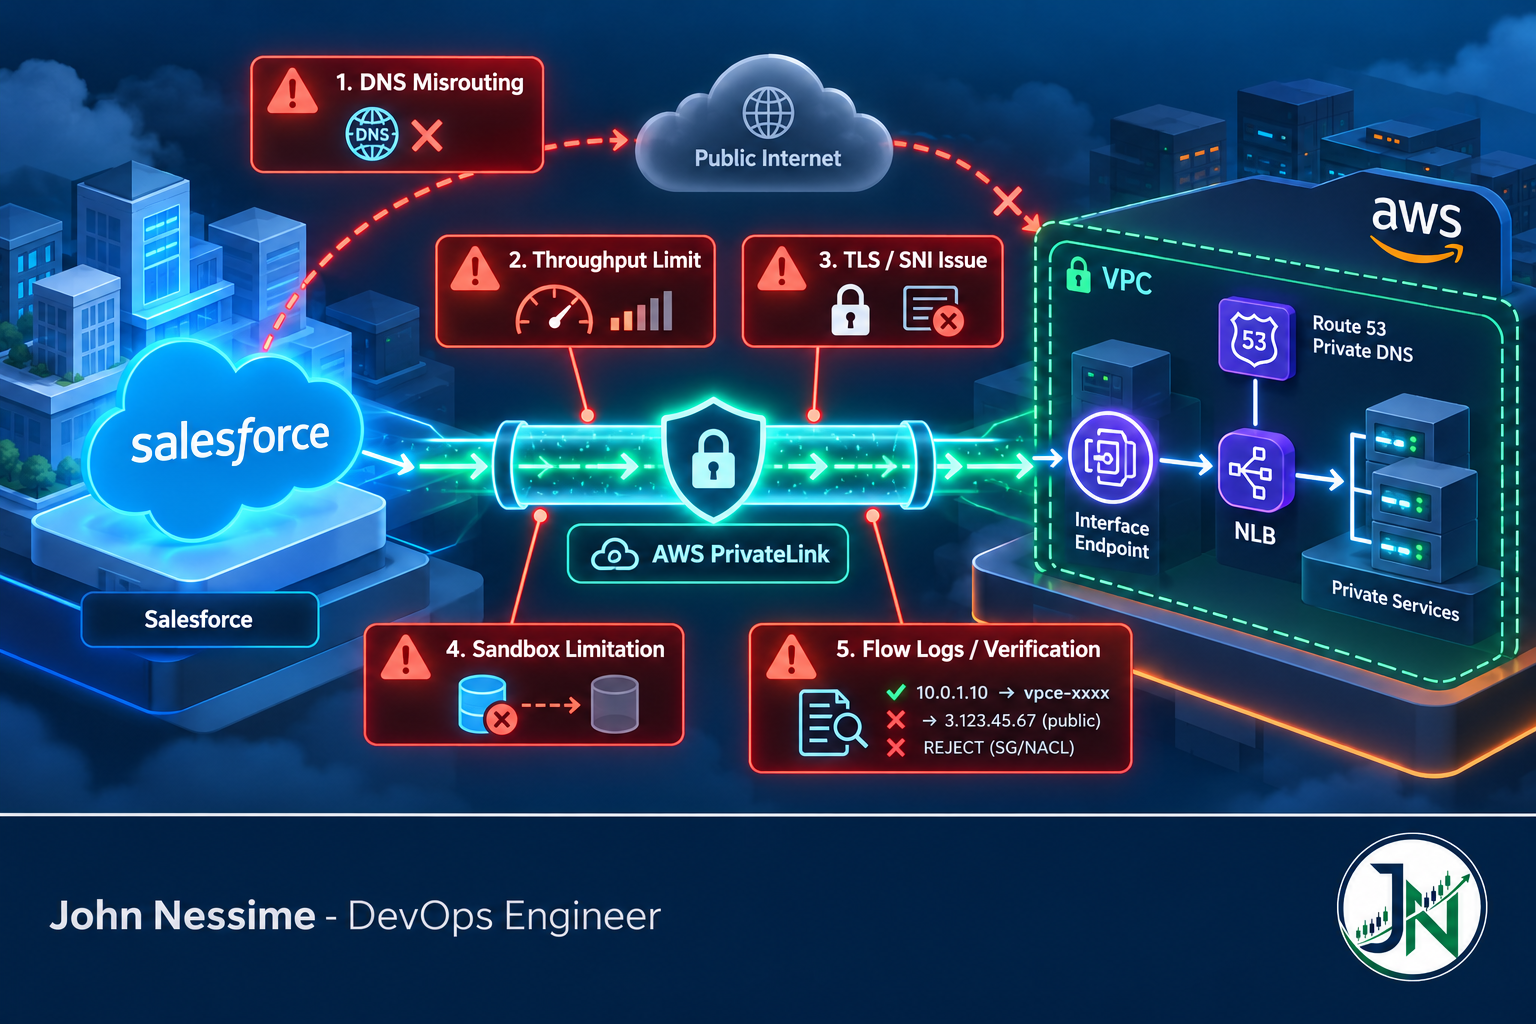
Salesforce AWS PrivateLink: The Failures Nobody Warns You About

Salesforce Private Connect over AWS PrivateLink does not fail loudly. It fails by working: green statuses, successful callouts, and packets still crossing the public internet because one DNS record was wrong. Here are the six failure families that actually bite, and how to prove your traffic is private.
Continue ReadingSalesforce AWS PrivateLink: The Failures Nobody Warns You About

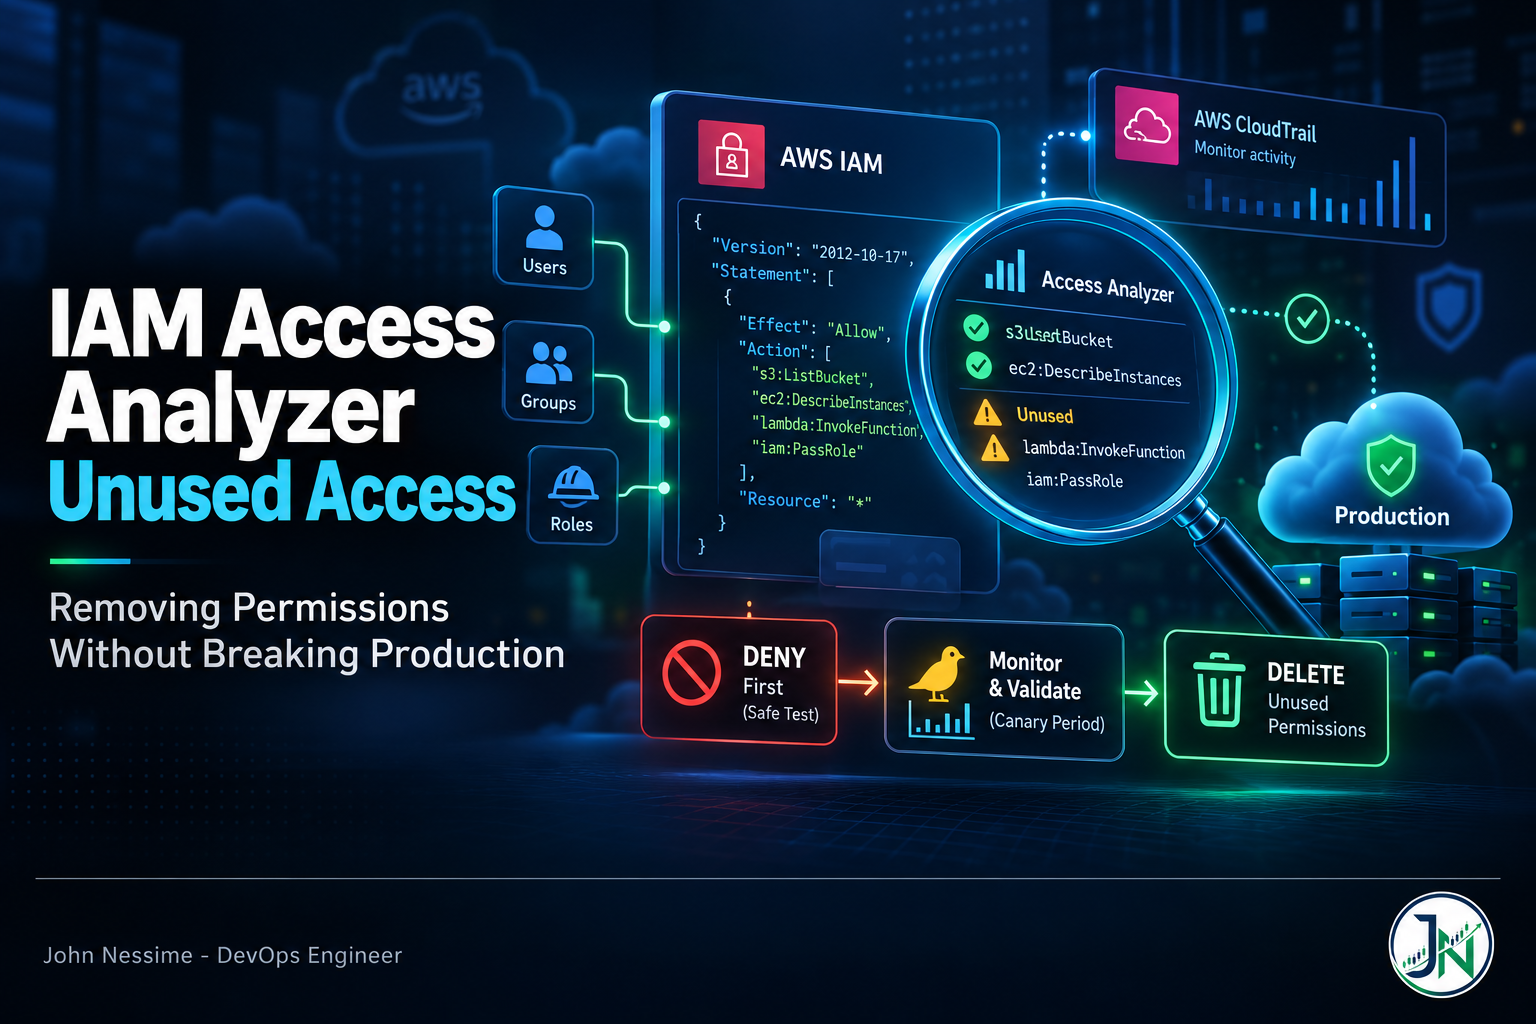
IAM Access Analyzer Unused Access: Removing Permissions Without Breaking Production

Unused access findings tell you what AWS did not record activity for, which is not the same as what your workload does not need. Here are the four blind spots in the underlying data, and a deny-before-delete procedure that lets you trim IAM permissions with a one-call rollback.

Continue ReadingIAM Access Analyzer Unused Access: Removing Permissions Without Breaking Production

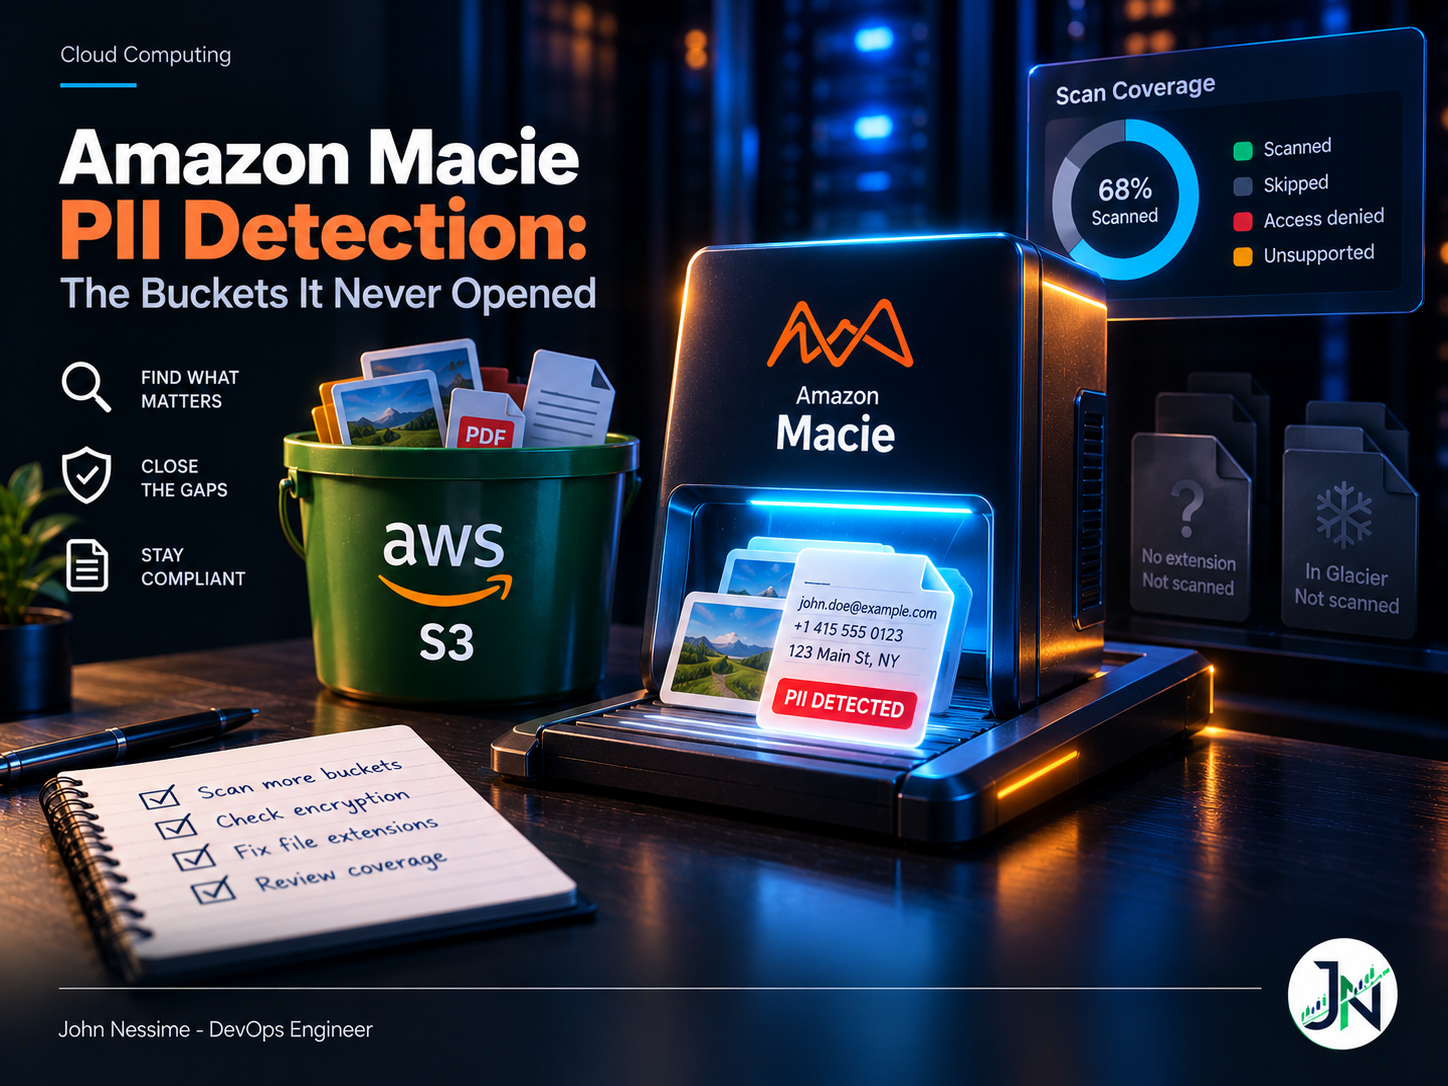
Amazon Macie PII Detection: The Buckets It Never Opened

A Macie bucket labeled "Not sensitive" often just means Macie never read it. Extensionless objects, unsupported storage classes, unreachable KMS keys and quota truncation all produce silence that looks identical to a clean result. Here's how to measure coverage, fix the four gaps, tune identifiers, and keep the bill honest.

Continue ReadingAmazon Macie PII Detection: The Buckets It Never Opened

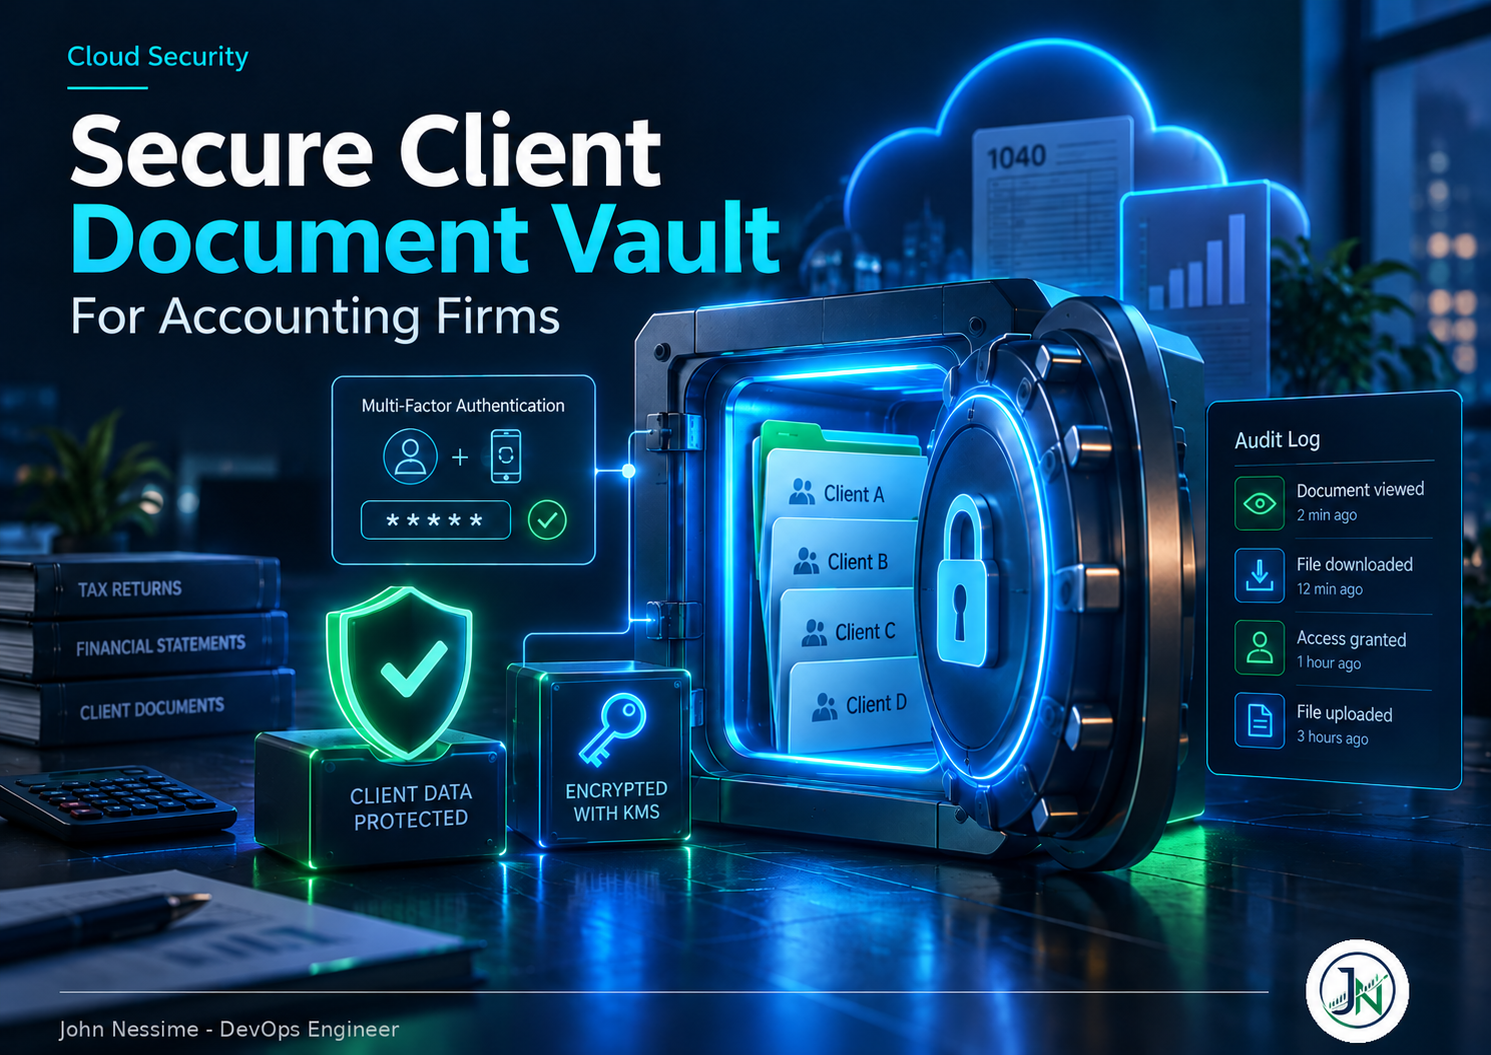
Building a Secure Client Document Vault Your Accounting Firm Can Defend

Most accounting-firm document vaults do not fail at the bucket. They fail at the edges: a download link that outlives the engagement, a KMS key policy as wide as the bucket policy, a retention lock that cannot be undone, and an audit trail nobody switched on. Six failure families, and the control that closes each.

Continue ReadingBuilding a Secure Client Document Vault Your Accounting Firm Can Defend

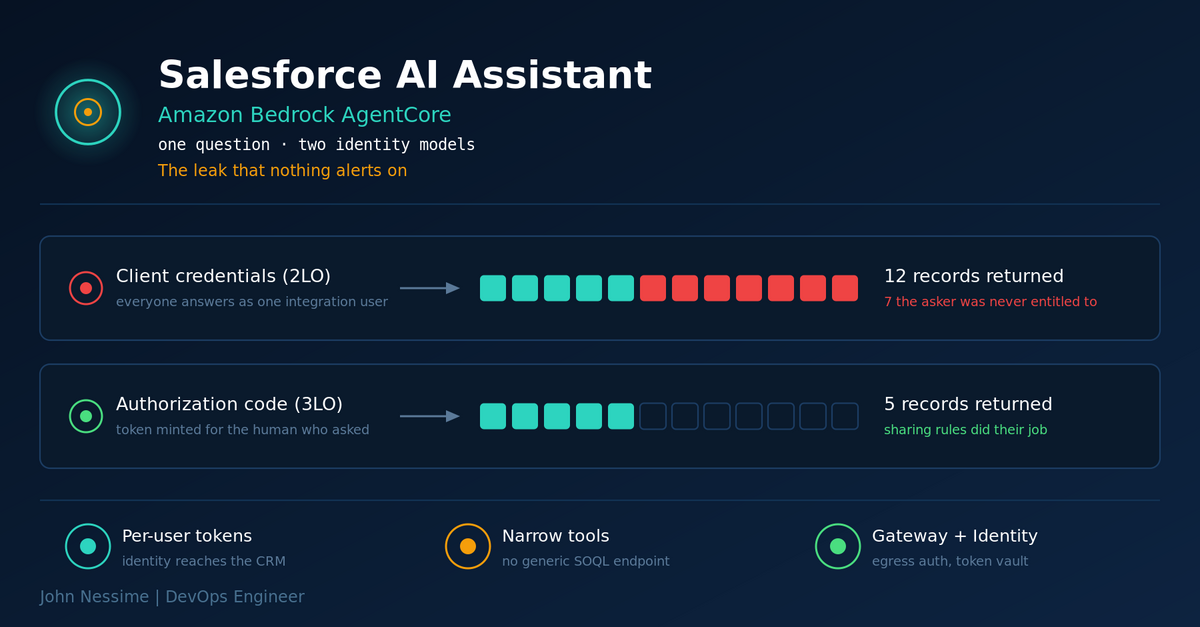
Building a Salesforce AI Assistant on Amazon Bedrock Without Leaking Your CRM

The demo works, then someone sees records they shouldn't. Nothing errors. Here's how to build a Salesforce AI assistant with Amazon Bedrock that respects your sharing model: which doors AWS and Salesforce just closed, why identity propagation is the failure mode that bites, and how to shape the tool surface so the agent can't wander.

Continue ReadingBuilding a Salesforce AI Assistant on Amazon Bedrock Without Leaking Your CRM

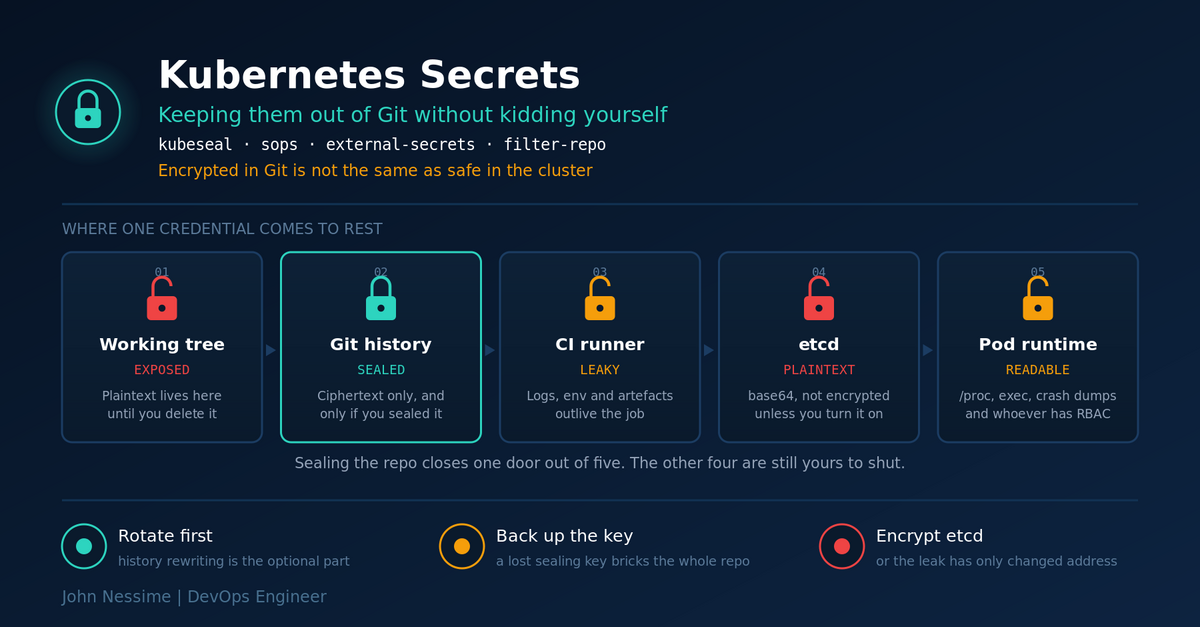
Keep Kubernetes Secrets Out of Git Without Kidding Yourself

Encrypting a Secret before you commit it only closes one of the five places that value comes to rest. Here is how to keep Kubernetes secrets out of Git properly: Sealed Secrets, SOPS and External Secrets compared honestly, the key-backup problem nobody plans for, and what to actually do when a credential is already in your history.

Continue ReadingKeep Kubernetes Secrets Out of Git Without Kidding Yourself

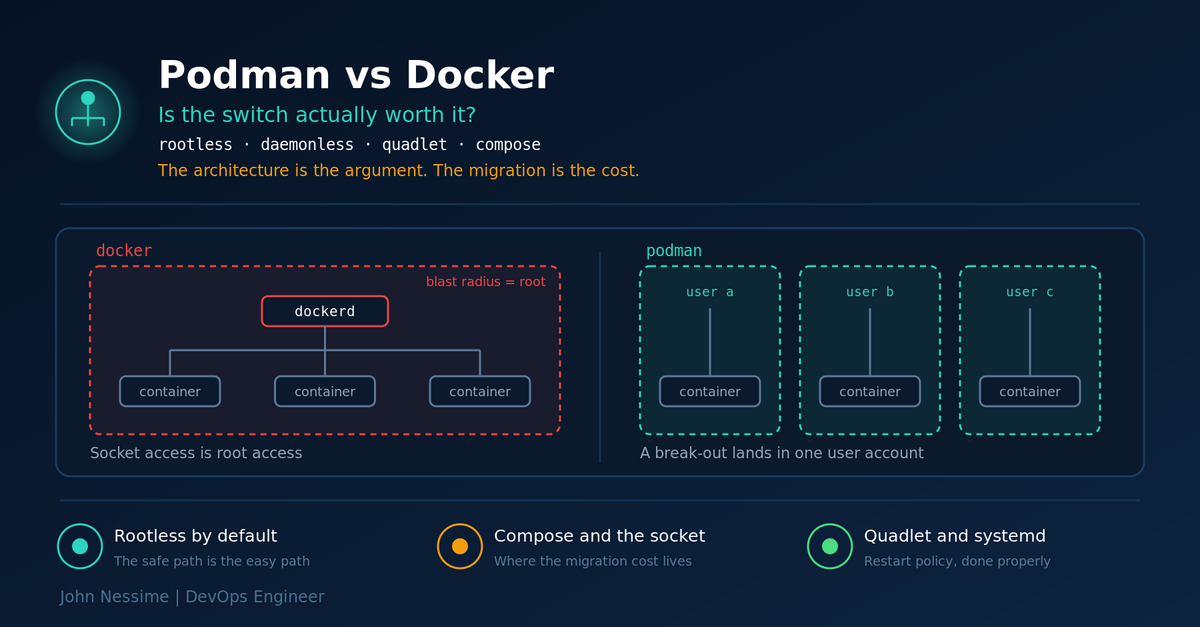
Podman vs Docker: Is the Switch Actually Worth It?

Podman is the better-designed container engine and Docker is the better-supported one. A working engineer's comparison: the architectural difference that drives everything, where each one wins and loses, the four things that genuinely break in a migration (compose, the Docker socket, privileged ports, restart on boot), and a decision procedure to run against your own setup.

Continue ReadingPodman vs Docker: Is the Switch Actually Worth It?