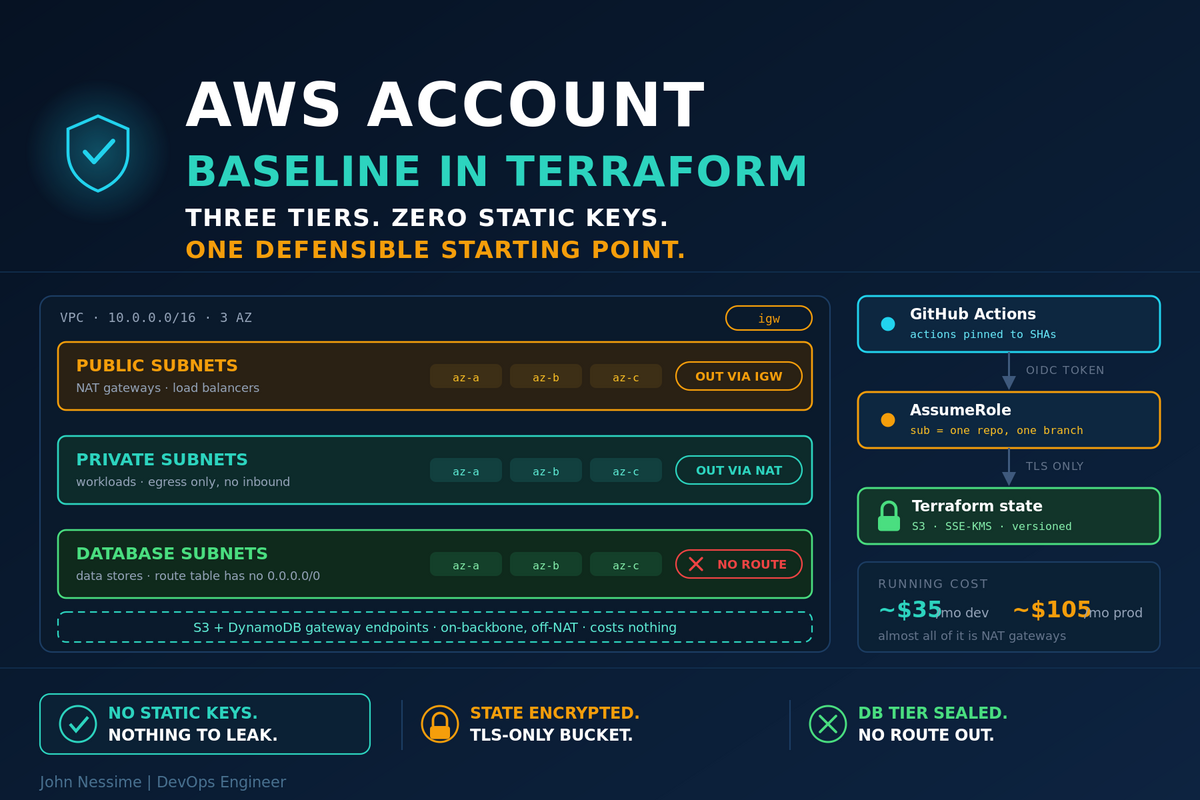
Bootstrap a VPS With Ansible in One Run Without Locking Yourself Out

A single Ansible run can take a blank VPS to a hardened, reproducible server. The hard part is not the tasks, it is the order. Here is the ordering that keeps you logged in, the failures that pass green and bite two weeks later, and how to make the second run as safe as the first.
Continue ReadingBootstrap a VPS With Ansible in One Run Without Locking Yourself Out

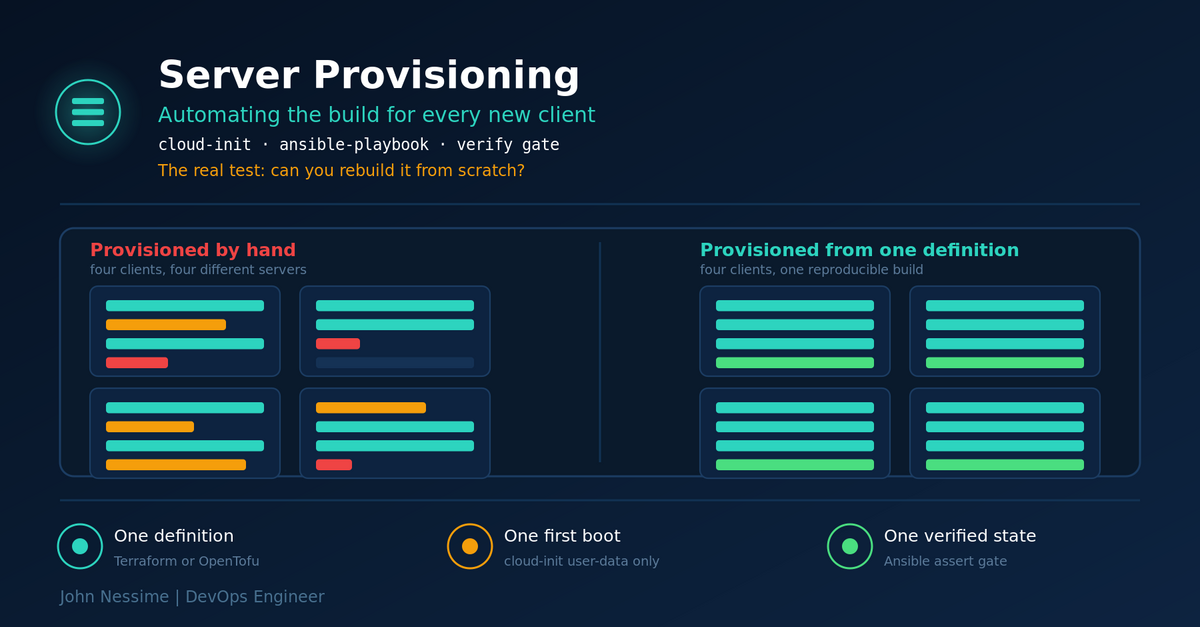
Automating Server Provisioning for New Clients Without Building a Snowflake Farm

Hand-built client servers fail quietly: you only find out they were never reproducible on the day you need to rebuild one. Here is how to automate server provisioning for new clients using cloud-init for first boot, Ansible for convergence, per-client secrets and a verification gate that refuses to hand over a half-built box.

Continue ReadingAutomating Server Provisioning for New Clients Without Building a Snowflake Farm

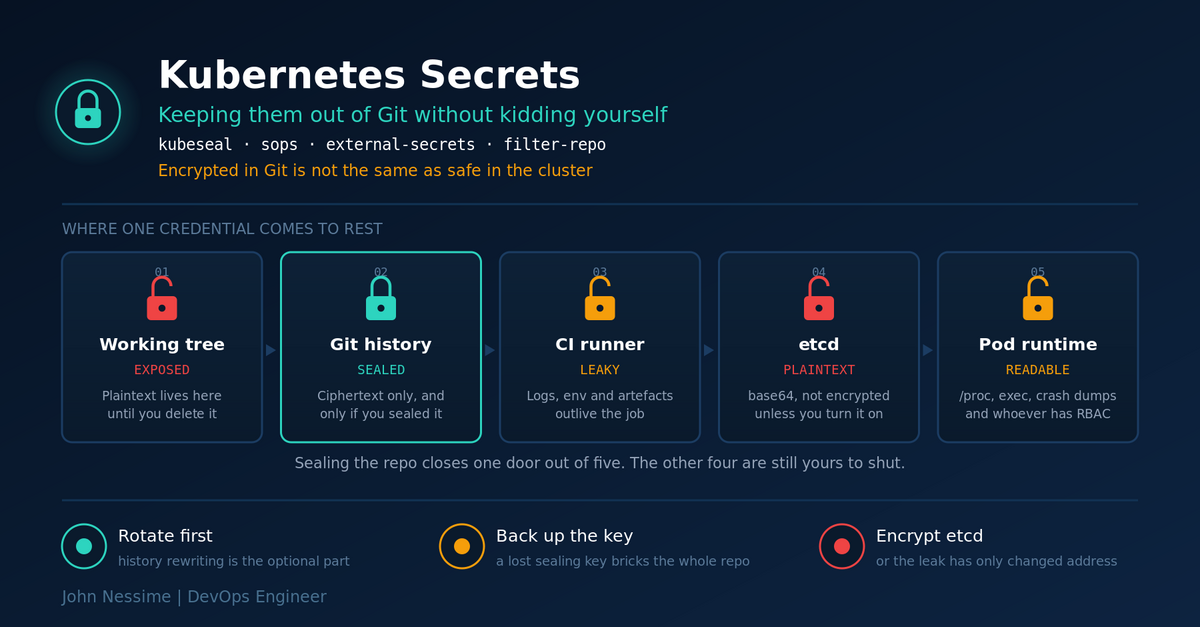
Keep Kubernetes Secrets Out of Git Without Kidding Yourself

Encrypting a Secret before you commit it only closes one of the five places that value comes to rest. Here is how to keep Kubernetes secrets out of Git properly: Sealed Secrets, SOPS and External Secrets compared honestly, the key-backup problem nobody plans for, and what to actually do when a credential is already in your history.

Continue ReadingKeep Kubernetes Secrets Out of Git Without Kidding Yourself