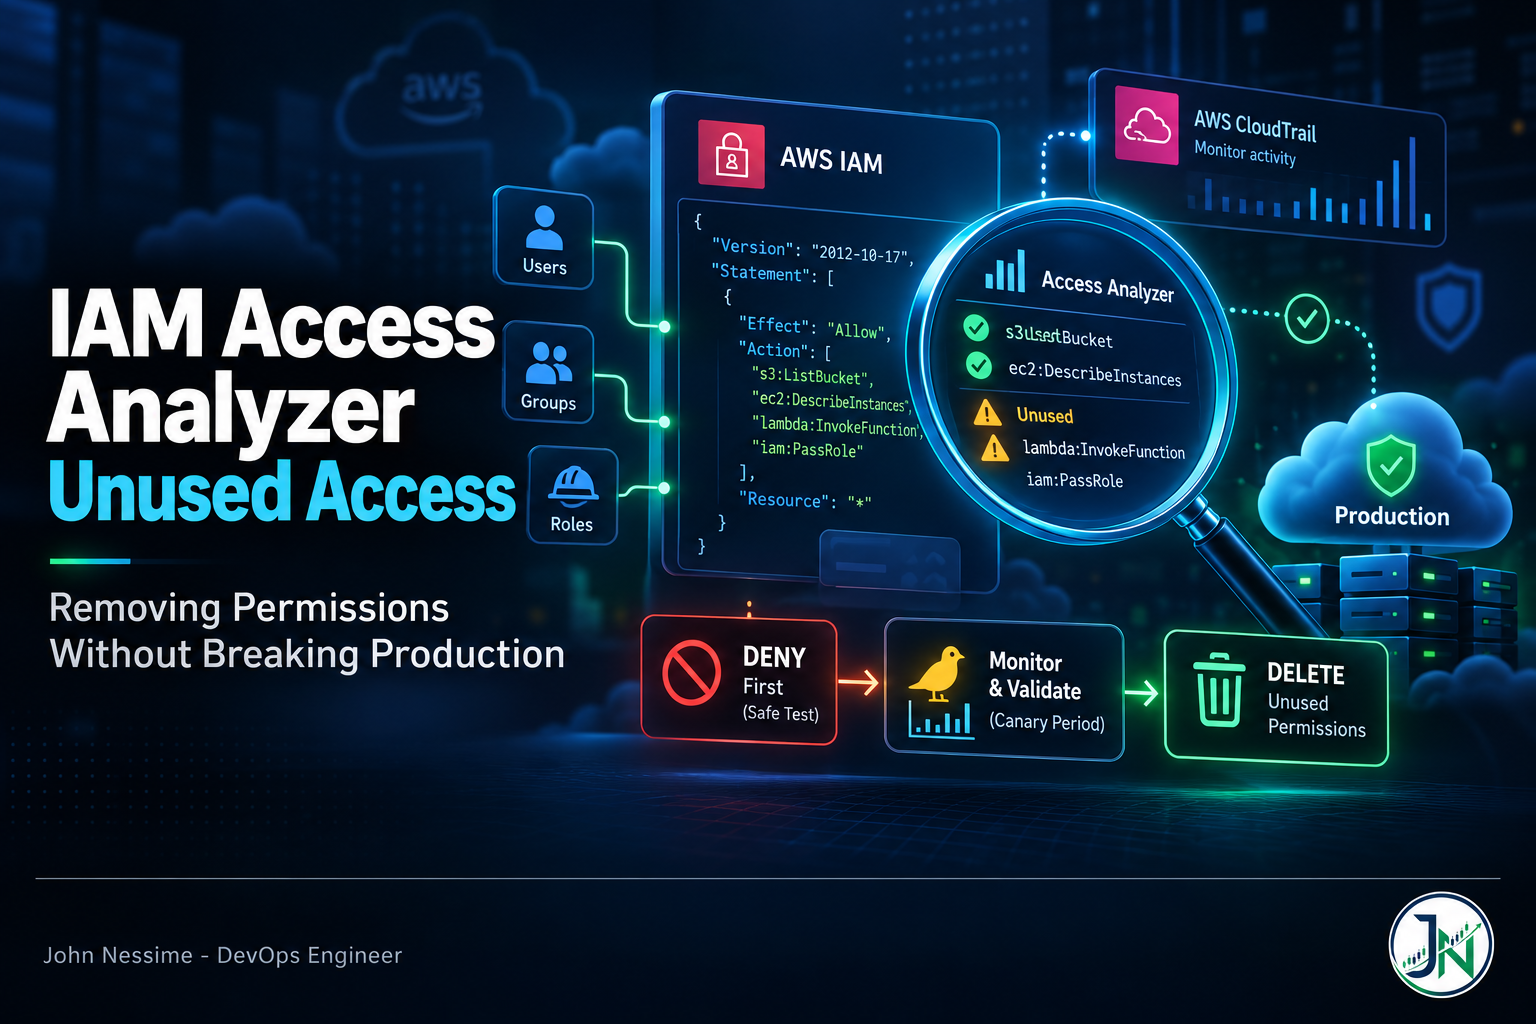
IAM Access Analyzer Unused Access: Removing Permissions Without Breaking Production

Unused access findings tell you what AWS did not record activity for, which is not the same as what your workload does not need. Here are the four blind spots in the underlying data, and a deny-before-delete procedure that lets you trim IAM permissions with a one-call rollback.

Continue ReadingIAM Access Analyzer Unused Access: Removing Permissions Without Breaking Production

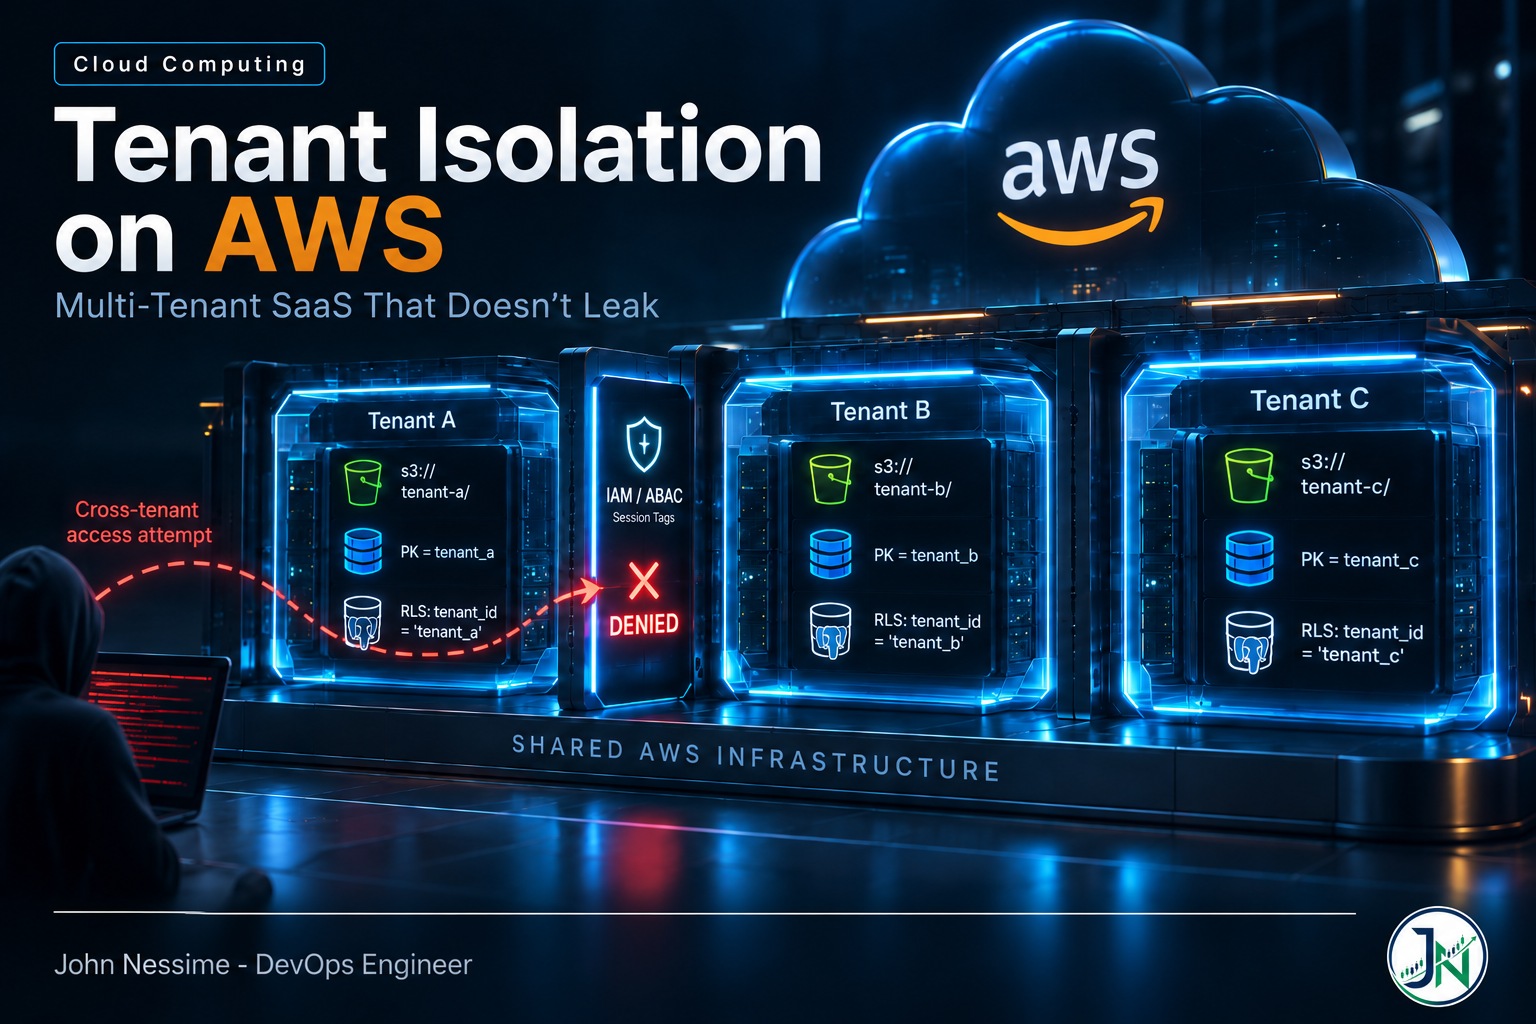
Tenant Isolation on AWS: Building a Multi-Tenant Workshop Platform That Doesn’t Leak

A missing tenant filter doesn't throw an error, it returns a 200 with too many rows. This is how to build a multi-tenant workshop management platform on AWS where the isolation boundary sits below your application code: STS session tags feeding IAM conditions, DynamoDB leading keys, scoped S3 prefixes, forced PostgreSQL row-level security, and a control plane that verifies each new tenant is fenced before anyone logs in.

Continue ReadingTenant Isolation on AWS: Building a Multi-Tenant Workshop Platform That Doesn’t Leak