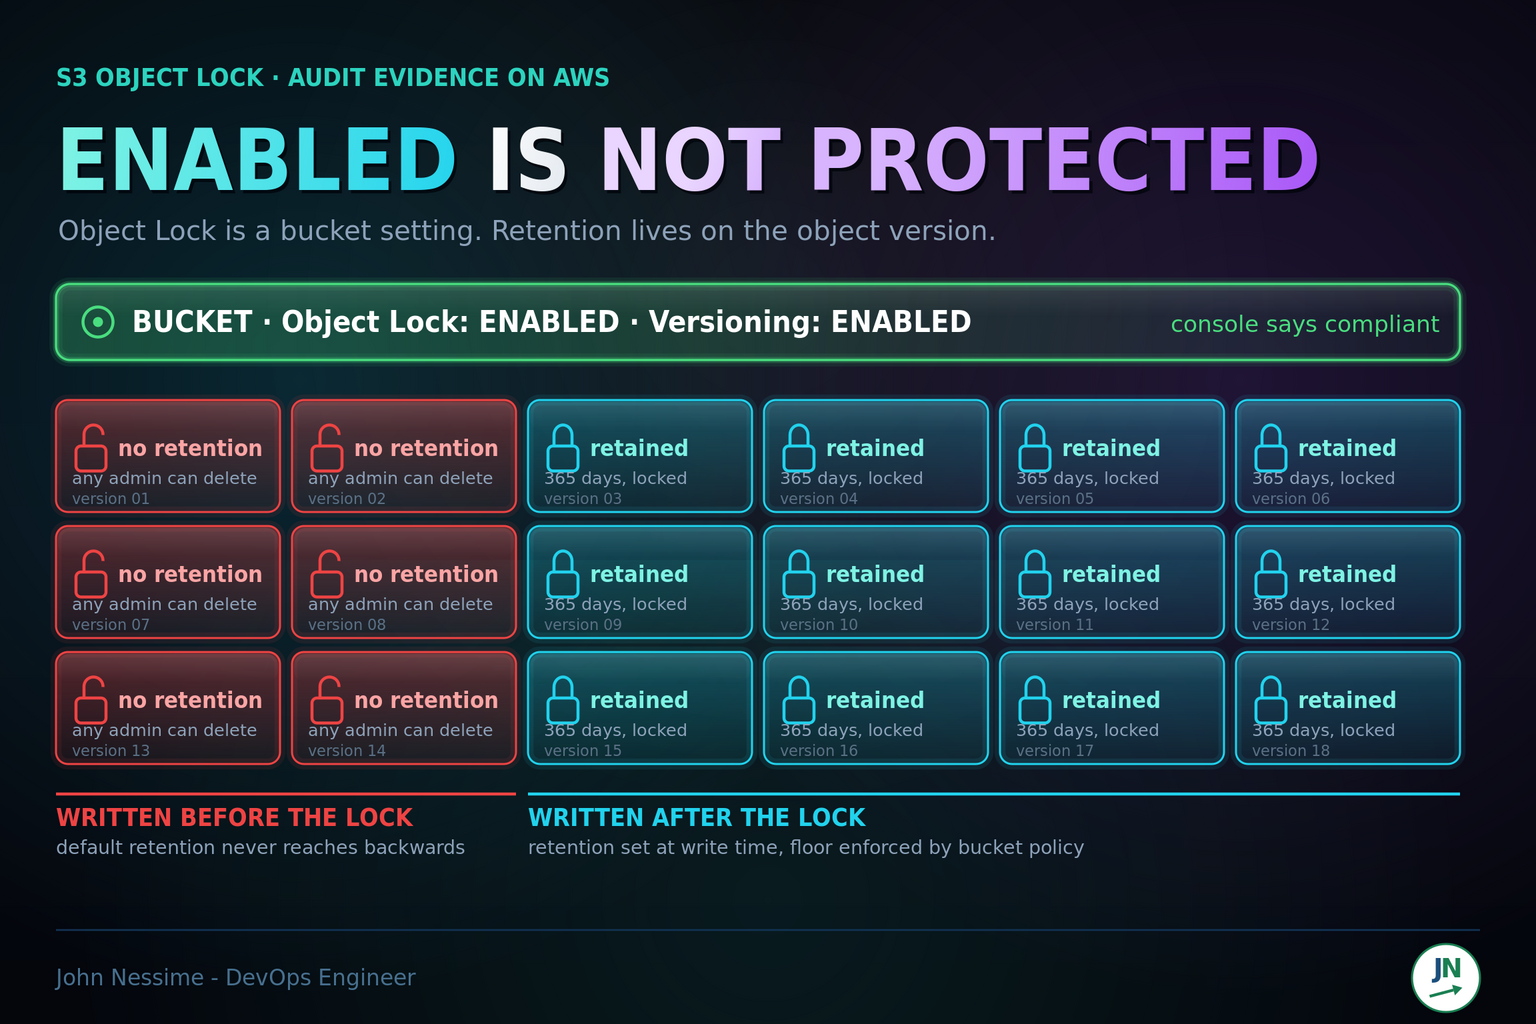
Building an Audit Evidence Repository on AWS: Immutable Retention Without Regret

Enabling S3 Object Lock on a bucket does not protect the objects already in it. This is how to build an audit evidence repository on AWS that survives the question auditors actually ask, covering retention modes you cannot undo, delete markers that hide protected versions, chain of custody, and the storage bill compliance mode makes permanent.
Continue ReadingBuilding an Audit Evidence Repository on AWS: Immutable Retention Without Regret

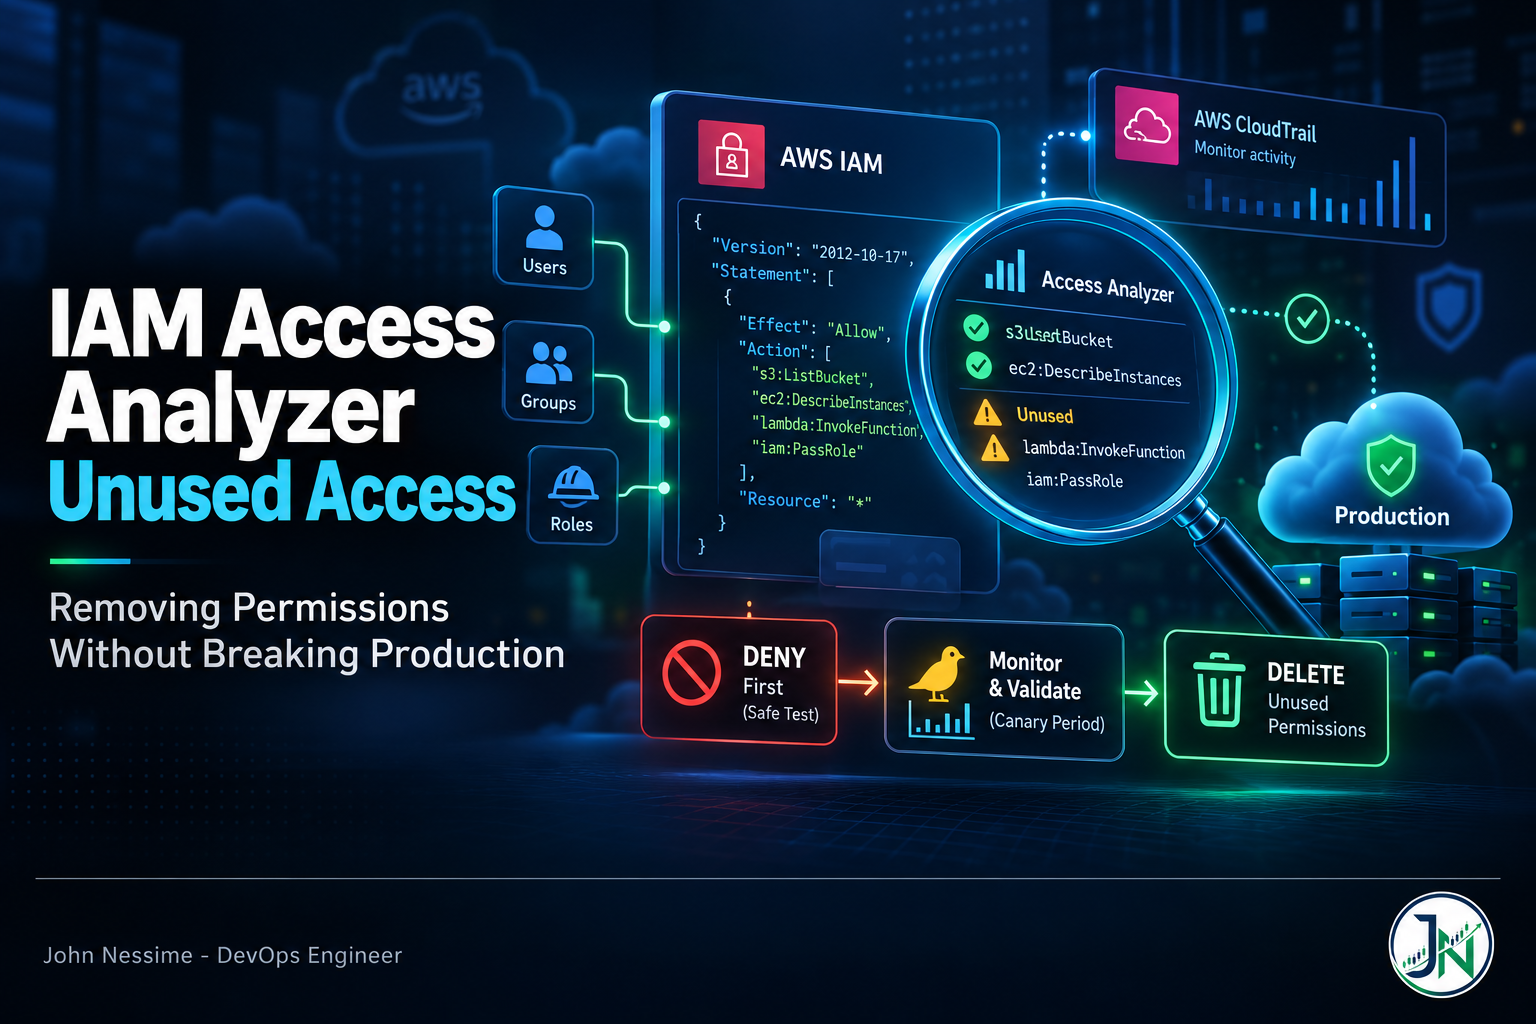
IAM Access Analyzer Unused Access: Removing Permissions Without Breaking Production

Unused access findings tell you what AWS did not record activity for, which is not the same as what your workload does not need. Here are the four blind spots in the underlying data, and a deny-before-delete procedure that lets you trim IAM permissions with a one-call rollback.

Continue ReadingIAM Access Analyzer Unused Access: Removing Permissions Without Breaking Production

Building a Secure Client Document Vault Your Accounting Firm Can Defend

Most accounting-firm document vaults do not fail at the bucket. They fail at the edges: a download link that outlives the engagement, a KMS key policy as wide as the bucket policy, a retention lock that cannot be undone, and an audit trail nobody switched on. Six failure families, and the control that closes each.

Continue ReadingBuilding a Secure Client Document Vault Your Accounting Firm Can Defend